Categories
Saved Web Pages

Exclusive: FBI probes use of Israeli firm’s spyware in personal and government hacks – sources

?m=02&d=20200131&t=2&i=1483719354&r=LYNX

(Reuters) – The FBI is investigating the role of Israeli spyware vendor NSO Group Technologies in possible hacks on American residents and companies as well as suspected intelligence gathering on governments, according to four people familiar with the inquiry.

FILE PHOTO: Activists and journalists protest outside the Attorney General’s Office (PGR) after a criminal complaint following a report that their smartphones had been infected with spying software sold to the government to fight criminals and terrorists in Mexico City, Mexico June 23, 2017. REUTERS/Carlos Jasso/File Photo

The probe was underway by 2017, when Federal Bureau of Investigation officials were trying to learn whether NSO obtained from American hackers any of the code it needed to infect smartphones, said one person interviewed by the FBI then and again last year.

NSO said it sells its spy software and technical support exclusively to governments and that those tools are to be used in pursuing suspected terrorists and other criminals. NSO has long maintained that its products cannot target U.S. phone numbers, though some cybersecurity experts have disputed that.

The FBI conducted more interviews with technology industry experts after Facebook filed a lawsuit in October accusing NSO itself of exploiting a flaw in Facebook’s WhatsApp messaging service to hack 1,400 users, according to two people who spoke with agents or Justice Department officials.

NSO said it was not aware of any inquiry.

“We have not been contacted by any U.S. law enforcement at all about any such matters,” NSO said in a statement provided by Mercury Public Affairs strategy firm. NSO did not answer additional questions about its employees conduct but previously said government customers are the ones who do the hacking.

A spokeswoman for the FBI said the agency “adheres to DOJ’s policy of neither confirming nor denying the existence of any investigation, so we wouldn’t be able to provide any further comment.”

Reuters could not determine which suspected hacking targets are the top concerns for investigators or what phase the probe is in. But the company is a focus, and a key issue is how involved it has been in specific hacks, the sources said.

Part of the FBI probe has been aimed at understanding NSO’s business operations and the technical assistance it offers customers, according to two sources familiar with the inquiry.

Suppliers of hacking tools could be prosecuted under the Computer Fraud and Abuse Act (CFAA) or the Wiretap Act, if they had enough knowledge of or involvement in improper use, said James Baker, general counsel at the FBI until January 2018.

The CFAA criminalizes unauthorized access to a computer or computer network, and the Wiretap Act prohibits use of a tool to intercept calls, texts or emails.

NSO is known in the cybersecurity world for its “Pegasus” software other tools that can be delivered in several ways. The software can capture everything on a phone, including the plain text of encrypted messages, and commandeer it to record audio.

A business strategy firm retained on behalf of Amazon.com Inc Chief Executive Jeff Bezos, FTI Consulting, said this month that NSO could have supplied the software it said Saudi Arabia used to hack Bezos’ iPhone.

The phone began sending out more data hours after it received a video from a WhatsApp account associated with Crown Prince Mohammed bin Salman, FTI said. Saudi Arabia called the FTI allegation “absurd,” and NSO said it was not involved. Other security experts said the data was inconclusive.

The FBI is investigating and has met with Bezos, a member of his team told Reuters. A Bezos spokesman did not respond to a request for comment.

FBI leaders have indicated that they are taking a hard line on spyware vendors.

At a briefing at FBI Washington headquarters in November, a senior cybersecurity official said that if Americans were being hacked, investigators would not distinguish between criminals and security companies working on behalf of government clients.

“Whether you do that as a company or you do that as an individual, it’s an illegal activity,” the official said.

In the counterintelligence aspect of the probe, the FBI is trying to learn if any U.S. or allied government officials have been hacked with NSO tools and which nations were behind those attacks, according to a Western official briefed on the investigation.

Outside of government, journalists, human rights activists and dissidents in several countries have been victims of attacks using NSO spyware, according to the University of Toronto’s Citizen Lab researchers.

In the past, NSO has denied involvement in some of those instances and declined to discuss others, citing client confidentiality requirements.

Reporting by Joseph Menn in San Francisco and Jack Stubbs in London; additional reporting by Raphael Satter and Chris Bing in Washington; editing by Greg Mitchell and Grant McCool

Categories
Saved Web Pages

Israeli Spy Companies Show Critical Link Between Flynn, Deripaska, and Senate Intelligence Committee Target Walter Soriano

ws-fn-3.png

Walter Soriano, a target of the U.S. Senate Intelligence Committee’s investigation into foreign election interference in 2016, appears to be a key middle-man connecting a network of Israeli hacking and surveillance firms to Russian oligarch Oleg Deripaska and former Trump National Security Adviser, Lt. Gen. Michael Flynn.

Under the umbrella of technology conglomerate NSO Group, two business entities appear critical to understanding the relationship between Soriano, Russian oligarchs, and Flynn. OSY Technologies and Circles.

Soriano’s connections to those firms deepen a mystery around the former Israeli intelligence officer and raise questions about American government officials who may have been involved with his activities.

Documents reviewed by Forensic News show that OSY Technologies is currently engaged in a contract with a law firm known for its work for the sanctioned oligarch, Deripaska. Sources familiar with the matter say the law firm is standing in for Deripaska in the contract, and report that the work related to the engagement involves Circles, the OSY subsidiary hacking firm. These details generate concern about American individuals who have contracted with OSY Technologies, NSO Group, and the related firms.

One of the American officials involved in this web is Lt. Gen. Flynn, the former National Security Advisor to President Donald Trump who was convicted of lying to the FBI at the onset of the Trump Administration. Public financial disclosures show that Flynn advised OSY Technologies from mid-2016 to January 2017. OSY Technologies (sometimes a stand-in name for the NSO Group conglomerate) is primarily a consortium of cyber-spy companies run by former Israeli intelligence officers. It is funded in significant part by enormous loans, at least one of which was issued by the bank Credit Suisse.

Several of Flynn’s aides and associates also work with other firms connected to Soriano. The Trump Department of Justice is controversially moving to drop Flynn’s guilty plea, an effort that has been met with skepticism by career prosecutors and the federal judge overseeing the case. Some uncharged conduct relating to Flynn’s work for Turkey appeared in his guilty plea as a representation of the Government’s leniency toward Flynn, but none of that information related to his work for Israeli-based intelligence companies.

The other company, a Bulgarian and Cyprus-based hacking and surveillance firm called Circles, is also an offshoot in the NSO Group corporate family. Its ties to Soriano run through his personal lawyer and his longtime business partner, demonstrated by filings related to the firm.

Circles has quietly been selling its services to governments around the world. It offers robust hacking and surveillance capabilities. Their software can be used to penetrate phones, read text messages, listen in on live phone calls, and track any user, all at a client’s request. As an NSO Group affiliate, Circles has tethered itself to malign actors, like the Saudi government, who have used its services to spy on private citizens, including journalists and political opponents. NSO Group is currently under criminal investigation by the FBI.

Now, Forensic News can reveal that Circles’ direct parent company, OSY Technologies–the firm for which Flynn worked–is actively contracted to work for Russian oligarch Oleg Deripaska. Deripaska is notably an associate of Paul Manafort who was personally sanctioned by the US in 2018 for his proximity to the Kremlin after its invasion of Ukraine in 2014. Sanctions on his major companies, however, were removed by the Trump Administration in 2019.

Circles, OSY Technologies, and NSO Group aren’t the only Israeli intelligence companies with unexplained ties to Trump campaign officials and Russian oligarchs. Other Israeli firms, including data analytics and social media manipulation firms such as Psy Group, reportedly offered the Trump Presidential campaign election assistance in 2016. That company is under criminal investigation in California regarding an election influence operation that was conducted on behalf of a local businessman.

Sources tell Forensic News that Psy Group was also contracted to work for Deripaska and another Russian oligarch, Dmitry Rybolovlev. Soriano has also reportedly worked for both men. These connections emerge as U.S. investigators have focused on whether these Israeli intelligence companies operated as intermediaries for alleged coordination between the Trump Campaign and Russia.

The Senate Intelligence Committee has for over a year attempted to interview Soriano regarding potential foreign election assistance offered to the 2016 Trump presidential campaign. His connections to the Israeli intelligence firms, discovered through a maze of public and private documents compiled by Forensic News, suggest Soriano is more deeply involved in entities connected to Deripaska than previously understood.

The Committee sought information from Soriano to explain those connections and other activities related to the 2016 U.S. Presidential election. In recent weeks, Forensic News has spoken to multiple sources who indicate Soriano and Deripaska have a closer relationship than what has been publicly reported, and that the Committee’s interest in Soriano was not a mere coincidence.

The sources–who provided details to supplement public documents and existing reporting–paint a picture positioning Walter Soriano at the center of a large, international web connecting hackers and private spies to Russian oligarchs, high-profile Israelis, and Trump administration officials.

Walter Soriano

Walter Soriano picture

Exclusive image of Walter Soriano

Soriano is a businessman and former Israeli military intelligence officer. The Senate Intelligence Committee, which recently submitted its report on foreign interference in the 2016 election for a declassification review by the intelligence community, sent a letter to Soriano’s London address in 2019 asking for any and all communications he had with Deripaska and other figures.

The letter requested information about correspondences between Soriano and Deripaska’s associates, Israeli private intelligence companies like Psy Group and Black Cube, Michael Flynn, and other Trump-world figures.

Forensic News acquired the letter sent to Soriano, seen below:


In February, Soriano told the Telegraph that he never received the letter. But, according to sources, Soriano did receive it, and thought it was a fake. Forensic News understands that Soriano instructed his Washington-based attorney to contact the Senate Intelligence Committee in order to find out whether the document was authentic. The Committee affirmed that it was and that they were serious about pursuing their investigation and his testimony.

The Telegraph article reports Soriano’s lawyers called the Senate to discuss the letter’s contents just days after it was sent. “The bi-partisan committee of US senators remains keen to interview Mr. Soriano,” the publication noted.

Soriano operates behind the scenes and actively avoids appearing in photographs, sources say, but his client list is eye-popping. Through another company he personally owns and manages called USG Security, he has worked for a number of Russian government-connected entities and oligarchs including Deripaska, Dmitry Rybolovlev, and Roman Abramovich.

Soriano’s circle in Israel is perhaps even more elite than in Russia. He is reportedly close to Prime Minister Benjamin Netanyahu and allegedly surveilled members of the police force who were investigating the Prime Minister for corruption, a charge that ended in an indictment for the embattled Israeli leader. Soriano unequivocally denies those allegations.

Other Israeli associates of Soriano include Netanyahu’s close confidants, Isaac Molho and Ari Harow. Harow served as Netanyahu’s Chief of Staff before he was convicted of fraud and breach of trust.

Soriano never responded to the Senate letter.

The 2020 Firms: FloLive & Circles

Forensic News reported in April on deep ties between FloLive, a London-based IT “connectivity and security” company, and Circles, a spyware affiliate of NSO Group. NSO Group is an Israeli spyware firm that has sold surveillance software to Arab and Western countries which have then spied on dissidents allegedly including Jamal Khashoggi. FloLive and Circles shared principal shareholders and employees. At one point, both companies were owned by the same offshore corporate entity.

The two founders of Circles, Boaz Goldman and Nadia Ropleva, are now leaders at FloLive. That move is striking, as the missions for the two companies couldn’t be more divergent. Circles develops tools to hack and surveil; FloLive is involved in cybersecurity and connectivity. FloLive explicitly claims it offers protection against the exact type of hacking that Circles exploits, an intrusion referred to as “SS7” hacking.

Numerous employees from Circles have made the jump to FloLive, and vice-versa. FloLive even posted a picture on their Facebook page showing employees playing a game of soccer with staff from Circles.

But publicly, the two firms have not acknowledged any official ties.

What worries security experts is the nature of the divergent work. As FloLive works with clients in the U.K. and elsewhere to set up “connectivity protections,” it could be acting as a front group for hackers at Circles to have better access to those same networks. The more clients FloLive is responsible for protecting against cyberattacks, the more information could be passed to Circles in furtherance of its hacking efforts in Europe and around the world.

Now, Forensic News can reveal that two associates of Walter Soriano have ownership stakes in the London company, FloLive. Soriano, a close ally of Israeli Prime Minister Benjamin Netanyahu and his family and a security operative who has worked for multiple Russian oligarchs, has reportedly kept distance between himself and operations to which he oversees.

Documents from the United Kingdom show that Walter Soriano’s personal lawyer, Shlomo Rechtschaffen, as well as Soriano’s business partner, Doron Cohen, are both shareholders of FloLive. Rechtschaffen and Cohen also work for Soriano’s real estate business in London. Cohen separately partnered with Soriano in another real estate venture in Florida.

In a statement to Forensic News, Rechtschaffen denied that Soriano himself was affiliated in any way with FloLive, saying, “clients of my firm are not related to one another. As a matter of fact, Mr. Soriano had never heard the name Flo or any of the other names mentioned below, prior to your email. As to Mr. Doron Cohen, as a matter of fact, he did acquire the shares mentioned below, long before any engagement with Mr. Soriano, which was prior to his meeting Soriano.

But Mr. Rechtschaffen’s statement regarding Soriano and Cohen appears demonstrably false. According to incorporation documents filed with the state of Florida, Soriano partnered with Cohen in their Florida business venture in July 2016. That was months before Cohen obtained his shares in FloLive in December 2016, making the assertion that Cohen acquired his stake in FloLive before meeting Soriano impossible.

  • Note: Walter Soriano via Rechtschaffen has previously threatened to sue Forensic News, stating, “We see no alternative left but to issue proceedings. We put you on notice that we will rely on any further publications or articles as seriously aggravating the damage caused by the original Article and will invite the Court to increase the award for libel to reflect the malicious and calculated nature of your campaign against our client.” To date, no lawsuit has been initiated.
  • Forensic News is funded entirely by our readers. We don’t hide content behind paywalls or take money from corporate entities. Consider pledging your support so we can continue producing impactful investigative journalism.

Become a Patron!

The UK documents below indicate that Soriano’s connections to the hacking and surveillance firm Circles run deeper than publicly known.

Walter Soriano and Flo Live

FloLive shareholders include Flo Holdings

Walter Soriano's business partner Doron Cohen and Shlomo Rechtschaffen

Flo Holdings shareholders include Doron Cohen and Shlomo Rechtschaffen, two Soriano confidants.

Perhaps unintentionally, Rechtschaffen confirmed that FloLive has “involvement” with Circles. “I am Mr. Soriano’s lawyer and not his business partner, as wrongly stated by you… I have also provided legal advice for another client of mine, a company of the Flo Group (not the one mentioned in your email), long before their involvement with Circles,” he said.

He denied that Soriano had anything do with FloLive or Circles and didn’t explain why legal advice to a company would result in the lawyer receiving a large shareholder status in the firm.

Flochart showing Walter Soriano and his connections to FloLive

Michael Flynn and Walter Soriano

Soriano’s connections to Circles via his lawyer and business partner are of critical importance. Gen. Michael Flynn worked for the parent company of Circles, OSY Technologies, in 2016 and 2017.  As previously mentioned, the Senate Intelligence Committee sought communications between Soriano and Flynn. Flynn was forced to resign as National Security Adviser and pleaded guilty to lying to the FBI about his conversations with the Russian Ambassador.

OSY Technologies is managed by the directors of NSO Group, some of who are former members of the elite Israeli military signals intelligence, identified as Unit 8200. Circles is directly owned by OSY Technologies, according to documents acquired from Cyprus.

Another intriguing connection between Flynn and Soriano is Richard Frankel, a former U.S. intelligence official who left his position in the federal government to join Soriano’s private security firm USG Security in early 2016.

Frankel was a senior aide to Michael Flynn. One news report by ABC News–where Frankel is now a contributor–described Frankel as a “friend” of Flynn’s. It’s unclear if Frankel still works for USG Security, though a January 2017 book on cybersecurity listed Frankel as a “Managing Director” for that Soriano company (p. 15).

Frankel did not respond to a list of detailed questions. It is unclear whether Frankel’s departure from the U.S. intel community to join Soriano’s operation–around the same time Flynn began advising the Trump 2016 campaign and OSY Technologies and the same time Soriano’s USG began work for Rybolovlev–is related to the Senate Intelligence Committee’s request for communications between Soriano and Flynn.

Other connections between former Flynn aides and work they may have completed for Circles are also being explored. A spokesperson for the Senate Intelligence Committee did not respond when asked about the status of their investigation into Walter Soriano. Sidney Powell, an attorney for Michael Flynn, did not respond to questions about Flynn’s work for OSY Technologies.

Rechtschaffen denied that Soriano has ever had a relationship with Flynn stating, “Walter Soriano has never met, had not and does not have, any relationship whatsoever (directly or indirectly) with Mr. Flynn, hence no messages directly or indirectly have been required or ever passed.

Walter Soriano & Oleg Deripaska

Walter Soriano has associated with Deripaska for a number of years. Forensic News reported in 2019 that Soriano was hired by Deripaska’s company, Basic Element, to provide security for the 2014 Olympics at the airport in Sochi, Russia. The contract stipulated that Soriano’s USG Security had “direct control” of operations at the Sochi airport, which is majority-owned by Basic Element.

Parts of a subcontract for the Sochi deal reveal strict stipulations regarding Soriano and Deripaska, as seen below.

Walter Soriano subcontract

The subcontractors were to represent themselves as USG Security workers and mention Walter Soriano’s name to any Russian authorities

Walter Soriano confidentiality clause

The subcontract demands that the subcontractor not divert business from Deripaska and another major USG Security (Walter Soriano’s firm) client

Deripaska continues to contract with Israeli security firms for secretive work.

Forensic News has exclusively reviewed an invoice paid to OSY Technologies from a Moscow-based law firm known for its work for Deripaska and the Russian government. The invoice cited work the intelligence company, OSY Technologies, completed as recently as 2019, but began in early 2018. Sources involved with the matter told Forensic News that the law firm is a stand-in for Deripaska and there are indications in the invoice that the work began earlier than 2018.

The invoice shows that a project was paid for by the law firm, Egorov Puginsky Afanasiev & Partners (EPAP or EPAM in Russian). The document—on OSY Technologies letterhead—stated that funds were to be paid to a bank account at UniCredit Bulbank in Bulgaria controlled by OSY Technologies – the NSO Group offshoot. Included in the documents were bank account numbers for OSY Technologies.

Forensic News understands that the payment was for services completed by OSY Technologies’ subsidiary hacking company, the Bulgaria-based Circles, though the name Circles does not appear on the documents.

The invoices were sent to the head of the law firm’s Moscow branch, Elena Kuznetsova. A LinkedIn profile for Kuznetsova shows that she previously worked for Deripaska’s aluminum company, Rusal. The founder of the law firm, Dmitry Afanasiev, has worked for Deripaska’s companies for at least 14 years and even held a coveted position on the board of Rusal before stepping down when U.S. officials demanded Deripaska’s allies cede control of the company in exchange for lifting sanctions.

Forensic News is currently unable to publish the document, as the sources who provided the invoice feared that they could be in danger if it were released to the public. In a series of emails, Tom Clare, an American attorney representing Deripaska, flatly denied that his client has ever hired OSY Technologies or Circles, and rejected the claim that Deripaska has any relationship with the principals of Circles or that the Russian oligarch worked with Walter Soriano in any capacity after the 2014 Sochi Airport deal.

EPAP, the Moscow-based law firm, is also a close partner of the Russian state and has even worked for Russian President Vladimir Putin in an individual capacity. Nikolai Egorov, one of the name-sake founders of the firm, was classmates with Putin at Leningrad State University in the 1970s. He later went on to teach and was a professor to Russian Prime Minister Dmitry Mendvedev.

The other name-sake founder, Stanislav Puginsky, was handpicked by convicted Russian agent Maria Butina and her handler Alexander Torshin to attend the 2017 National Prayer Breakfast, chaired by newly-minted President Trump. Butina was recently deported to Russia after serving prison time on espionage-lite charges.

EPAP has been a successful endeavor for Egorov, and a deep-dive into the law firm by Law.com in 2007 stated that it acts as “a regular adviser to Putin’s government.”

But the firm’s U.S. ties raise more questions about connections between Trump associates and Deripaska. Records show EPAP’s U.S. branch represented Deripaska in a joint effort with Trump attorney Marc Kasowitz in a U.S. lawsuit filed by one of Deripaska’s companies. Kasowitz represented Trump in his personal capacity during the Mueller Investigation and has reportedly represented Trump and his businesses for decades. The shared representation of Deripaska and Trump made headlines in mid-2017.

Most remarkable about the contract between EPAP and OSY Technologies is that it puts Gen. Michael Flynn squarely in the middle of multiple figures that are still of interest to investigators. As mentioned, Flynn worked for OSY Technologies through January 2017. The agreement seen by Forensic News between EPAP and OSY Technologies began in 2018, though the full nature of the relationship is unknown.

Flochart showing connections to Deripaska, Flynn, and OSY Technologies

Neither the Mueller Report nor any other public investigative report has detailed Flynn’s payment from foreign firms that also receive money from Deripaska. While Flynn’s plea agreement involved admissions that he conducted foreign work for Turkey in violation of laws about lobbying disclosure, the document made no reference to Flynn’s work with Israeli technology firms—a curious omission, especially in light of further revelations that Mueller examined whether George Papadopoulos (a Trump campaign foreign policy advisor) was an unregistered agent of Israel.

Flynn is not the only name with tenuous connections to Deripaska and Trump advisers. Georgiy Oganov, one of the aides who sources told us briefs Deripaska on information obtained by Circles and OSY Technologies, was mentioned in the Mueller Report. The Special Counsel documented a January 2017 meeting in Spain between Oganov and former Trump campaign manager Paul Manafort.

Another thread tying the three together: Manafort, Deripaska, and Oganov were all caught up in a controversy about recordings made by a Russian escort, Nastya Rybka, in 2016. Forensic News has learned that Walter Soriano may have been involved in that controversy as well.

Soriano, Oganov & Deripaska’s Mistress

Deripaska and his mistress Nastya Rybka.

Nastya Rybka and Oleg Deripaska
Courtesy: New Europe

Rybka, a Belarusian escort and self-described “sex coach” who had a relationship with Deripaska, claimed in 2018 to have audiotapes showing coordination between the Trump campaign and Russia after her monthslong affair with Deripaska in mid-2016 and early 2017.

She was arrested in Thailand in 2018 after she famously published a video taken in August 2016 of Deripaska discussing U.S. relations on a yacht with the Russian Deputy Prime Minister, Sergei Prikhodko. The woman claimed to have other video and audio recordings connecting Deripaska to Paul Manafort, and allegedly recorded Deripaska discussing election interference activities.

During the Mueller probe, the FBI unsuccessfully sought to speak with Rybka. She was later extradited back to Russia, where she was forced to publicly apologize to Deripaska at the Moscow airport.

An Intelligence Online report in late 2019 stated that Walter Soriano was involved in the Rybka affair at the behest of Deripaska, aiding in Deripaska’s effort to obtain the sensitive materials possessed by Rybka. Two sources familiar with this episode confirmed that Soriano was indeed involved, directly or indirectly, in attempting to silence Rybka. Rechtschaffen denied these claims.

Russian agents told Rybka to keep quiet about Deripaska, and the other audiotapes she claimed to have in her possession have never been published. Social media posts indicate that Rybka now resides in Moscow and runs an “online school for seduction.” Reached by Forensic News via the messaging app WhatsApp, Rybka declined to comment on anything political, stating that she would only speak about her commercial activities.

Russian opposition leader Alex Navalny revealed more of Rybka’s audio in 2019. Recordings make clear that Deripaska’s associates–including Georgiy Oganov–plotted the arrest of Rybka. “What we are interested in is that these people be kept in jail,” Oganov can be heard saying to an unknown lawyer named William.

Given Oganov’s reported service as Deripaska’s intermediary to Soriano and the inclusion of his name in both the Mueller Report and the Senate’s letter to Soriano, his discussion of silencing Rybka adds credence to allegations Soriano was involved in Rybka’s plight.

The US government has since determined that Oganov is a critical intermediary for Deripaska. As noted above, Special Counsel Robert Mueller’s report on Russian interference in the 2016 election detailed a meeting between Paul Manafort and Oganov. The meeting took place in January 2017, after Russian efforts to interfere on Trump’s behalf had been revealed. The European connection was initially denied by Manafort, but U.S. investigators were not convinced.

Mueller reported that the men were slated to discuss “recreating the old friendship” between Deripaska and Manafort at the January meeting, which allegedly took place in Madrid. That Manafort was willing to meet with Oganov after his own expulsion from the Trump campaign as well as recently-published allegations of improper ties between Trump and Russia suggests Oganov was a person of critical importance to Manafort. The meeting was also arranged by Konstantin Kilimnik, an alleged Russian agent who acted as a go-between for Manafort and Deripaska during the campaign season:

Mueller report passage regarding Georgiy Oganov

Allegations that Oganov is both a critical intermediary between Deripaska and Manafort and Deripaska and Israeli intelligence firms have significant consequences. Manafort’s transmission of voter and polling data to alleged GRU-agent Kilimnik in 2016 looks more compelling in light of this new information. Mueller’s team was unable to determine (V. 1, p. 131) what happened to the polling data after Manafort gave it to Kilimnik.

It is notable that the Senate Intelligence Committee, led by Republican Chairman Richard Burr and Democratic Ranking Member Mark Warner, requested information from Soriano on his communications with many of these individuals. The Committee finalized the last section of its investigation into foreign interference in the 2016 Presidential Election just weeks ago, as Burr was forced to step down amidst allegations of insider trading.

The final section was submitted for declassification review on Burr’s last day in his role as Committee Chair. The Republican-led Committee has been known for its quiet, bipartisan work throughout the Trump Administration: its Republican majority notably issued a subpoena to Donald Trump, Jr. in June 2018, despite fierce opposition from President Trump.

The final section of the report, reportedly approximately 1000 pages, is said to detail a counterintelligence investigation conducted into the Trump Campaign’s connections with foreign actors. Such an investigation may be more extensive than the criminal investigation conducted by Robert Mueller, as counterintelligence investigations typically have a wider scope than criminal ones.

The Senate Intelligence Committee Report is slated to be released publicly–with redactions–in the coming weeks.

When asked whether Walter Soriano features in the upcoming report, both Senators Burr and Warner declined to comment.

Forensic News is funded entirely by our readers. We don’t hide content behind paywalls or take money from corporate entities. Consider pledging your support so we can continue producing impactful investigative journalism.

Become a Patron!

Categories
Saved Web Pages

Aretha Franklin Was Tracked By the FBI for 40 Years. Here’s What’s In Her File

b7b32fd7217502a039199494faae5f54

The agency tried — and failed — for decades to tie the Queen of Soul to “extremists”

Categories
Saved Web Pages

CIA betrayed informants with shoddy covert comms websites

shutterstock_cia_logo.jpg

For almost a decade, the US Central Intelligence Agency communicated with informants abroad using a network of websites with hidden communications capabilities.

The idea being: informants could use secret features within innocent-looking sites to quietly pass back information to American agents. So poorly were these 885 front websites designed, though, according to security research group Citizen Lab and Reuters, that they betrayed those using them to spy for the CIA.

Citing a year-long investigation into the CIA’s handling of its informants, Reuters on Thursday reported that Iranian engineer Gholamreza Hosseini had been identified as a spy by Iranian intelligence, thanks to CIA negligence.

“A faulty CIA covert communications system made it easy for Iranian intelligence to identify and capture him,” the Reuters report stated.

Word of a catastrophic failure in CIA operational security initially surfaced in 2018, when Yahoo! News reporters Zach Dorfman and Jenna McLaughlin revealed “a compromise of the agency’s internet-based covert communications system used to interact with its informants.”

The duo’s report indicated that the system involved a website and claimed “more than two dozen sources died in China in 2011 and 2012” as a result of the compromise. Also, 30 operatives in Iran were said to have been identified by Iranian intelligence, fewer of whom were killed as a consequence of discovery than in China.

Blocks of sequential IP addresses registered to apparently fictitious US companies were used to host some of the websites

Reuters found one of the CIA websites, iraniangoals[.]com, in the Internet Archive and told Citizen Lab about the site earlier this year. Bill Marczak, from Citizen Lab, and Zach Edwards, from analytics consultancy Victory Medium, subsequently examined the website and deduced that it had been part of a CIA-run network of nearly 900 websites, localized in at least 29 languages, and intended for viewing in at least 36 countries.

These websites, said to have operated between 2004 and 2013, presented themselves as harmless sources of news, weather, sports, healthcare, or other information. But they are alleged to have facilitated covert communications, and to have done serious harm to the US intelligence community and to those risking their lives to help the United States.

“The websites included similar Java, JavaScript, Adobe Flash, and CGI artifacts that implemented or apparently loaded covert communications apps,” Citizen Lab explains in its report. “In addition, blocks of sequential IP addresses registered to apparently fictitious US companies were used to host some of the websites. All of these flaws would have facilitated discovery by hostile parties.”

The websites were designed to look like common commercial publications but included secret triggering mechanisms to open a covert communication channel. For example, the supposed search box on iraniangoals[.]com is actually a password input field to access such its hidden comms functionality – which you’d never guess unless you inspected the website code to see the input field identified as type="password" or unless the conversion of text input into hidden • characters gave it away.

Entering the appropriate password opened a messaging interface that spies could use to communicate.

The encrypted messaging widgets from CIA can be found on websites in numerous languages, & technical fingerprints made it possible to find more websites within the network, even nearly a decade after they had been taken down, thanks to the @waybackmachine. Did the CCP know too? https://t.co/5CFa11mFbT

— Zach Edwards (@thezedwards) September 29, 2022

Citizen Lab says it has limited the details contained in its report because some of the websites point to former and possibly still active intelligence agents. It says it intends to disclose some details to US government oversight bodies. The security group blames the CIA’s “reckless infrastructure” for the alleged agent deaths. Zach Edwards put it more bluntly on Twitter.

“Sloppy ass website widget architecture plus ridiculous hosting/DNS decisions by CIA/CIA contractors likely resulted in dozens of CIA spies being killed,” he said.

What makes the infrastructure ridiculous or reckless is that many of the websites had similarities with others in the network and that their hosting infrastructure appears to have been purchased in bulk from the same internet providers and to have often shared the same server space.

“The result was that numerical identifiers, or IP addresses, for many of these websites were sequential, much like houses on the same street,” Reuters explained.

Such basic errors continue to trip up spy agencies. Investigative research group Bellingcat, for example, has used the sequential numbering of passports to help identify the fake personas of Russian GRU agents. It described this blunder as “terrible spycraft.”

And while numerically proximate or sequential identifiers may go unnoticed some of the time – security through obscurity – it only takes one double agent aware of the scheme to allow adversaries to connect the dots.

In the case of Iran, that’s what happened, according to Yahoo! News: “Though the Iranians didn’t say precisely how they infiltrated the network, two former US intelligence officials said that the Iranians cultivated a double agent who led them to the secret CIA communications system.”

The CIA did not respond to a request for comment. ®

A former NSA man has been charged with three counts of espionage. Jareh Sebastian Dalke, 30, of Colorado Springs, is accused of emailing three classified files to someone he thought was a foreign government agent but was in fact an undercover FBI agent.

Dalke left the NSA in July this year, and soon after attempted to leak documents he had stolen from the agency, prosecutors claim. According to the Justice Dept, Dalke claimed he “had taken highly sensitive information relating to foreign targeting of US systems, and information on US cyber operations, among other topics,” and wanted cryptocurrency in exchange for the files.

He was arrested on September 28 and was due to appear in court today. If convicted, he potentially faces the death penalty or any length of time behind bars.

Categories
Saved Web Pages

Convictions in FBI Sting of Politician Should Be Thrown Out, Legal Scholar Says

GettyImages-84611044-1.jpg

An Ohio politician who was ensnared in an FBI “sting” wants his two corruption-related convictions thrown out—a challenge that ought to prevail, says a legal scholar who has followed the case closely.

Lawyers for Alexander “P.G.” Sittenfeld, a former Cincinnati city councilman who was convicted of bribery and attempted extortion this summer, filed motions for acquittal and a new trial on Sept. 30 in the U.S. District Court in Cincinnati.

Epoch Times Photo Ken Katkin, professor of law at Northern Kentucky University. (Courtesy of Northern Kentucky University Chase School of Law)

While such post-trial motions are common, they rarely succeed. But Ken Katkin, a professor of law at Northern Kentucky University near Cincinnati, opined that Sittenfeld’s main argument is valid.

“I don’t think there was any crime here at all,” Katkin told The Epoch Times, predicting that Sittenfeld will eventually win a reversal. He thinks the prosecution of Sittenfeld was an “overreach,” resulting from the FBI’s making corruption cases a top priority.

Federal prosecutors didn’t immediately respond to a reporter’s emails requesting comment.

Controversies Followed Verdict

The latest actions in the case came days after a federal appeals court refused to allow Sittenfeld’s lawyers to dig into the cellphone of “Juror X,” who had repeatedly posted on Facebook about her jury experience during Sittenfeld’s trial.

After questioning Juror X and three other jurors, judges ruled they found no evidence that her actions tainted the verdict, so no further invasion of her privacy was warranted.

Although jurors convicted Sittenfeld on two federal charges in July, they acquitted him of four similar counts—a sign of the jury’s “obvious confusion” because the allegations related to the same patterns of conduct, his attorneys wrote.

Bogus Developers

Events leading to Sittenfeld’s prosecution began in 2018. Undercover FBI agents, posing as would-be real-estate developers, approached Sittenfeld and began discussing a project to redevelop a blighted area. They secretly recorded their conversations and also worked with an actual developer, who served as an informant.

The agents tried to “bait” Sittenfeld into violating campaign-finance laws, his lawyers wrote. But Sittenfeld “repeatedly declined non-compliant campaign contributions,” including cash, money orders, and trips to Miami, Las Vegas, and Nashville.

However, Sittenfeld did pledge to support the project that the fake developers, known as “Rob,” “Vinny,” and “Brian,” described. And the men eventually gave Sittenfeld a total of $40,000, authorities said. The funds went to Sittenfeld’s political action committee.

If that pattern of conduct constitutes bribery, “it means that substantially all campaign fundraising in this country” would fit that definition, Katkin said.

But that cannot be so, according to three U.S. Supreme Court cases, Katkin said. To violate federal corruption laws, an official must make an “explicit” promise to take a specific action, contingent upon payment or contributions, the court has ruled, Katkin said.

Katkin, who attended Sittenfeld’s trial every day, said those conditions weren’t met in Sittenfeld’s case. And because the project proposal was phony, there was never any vote or official action taken.

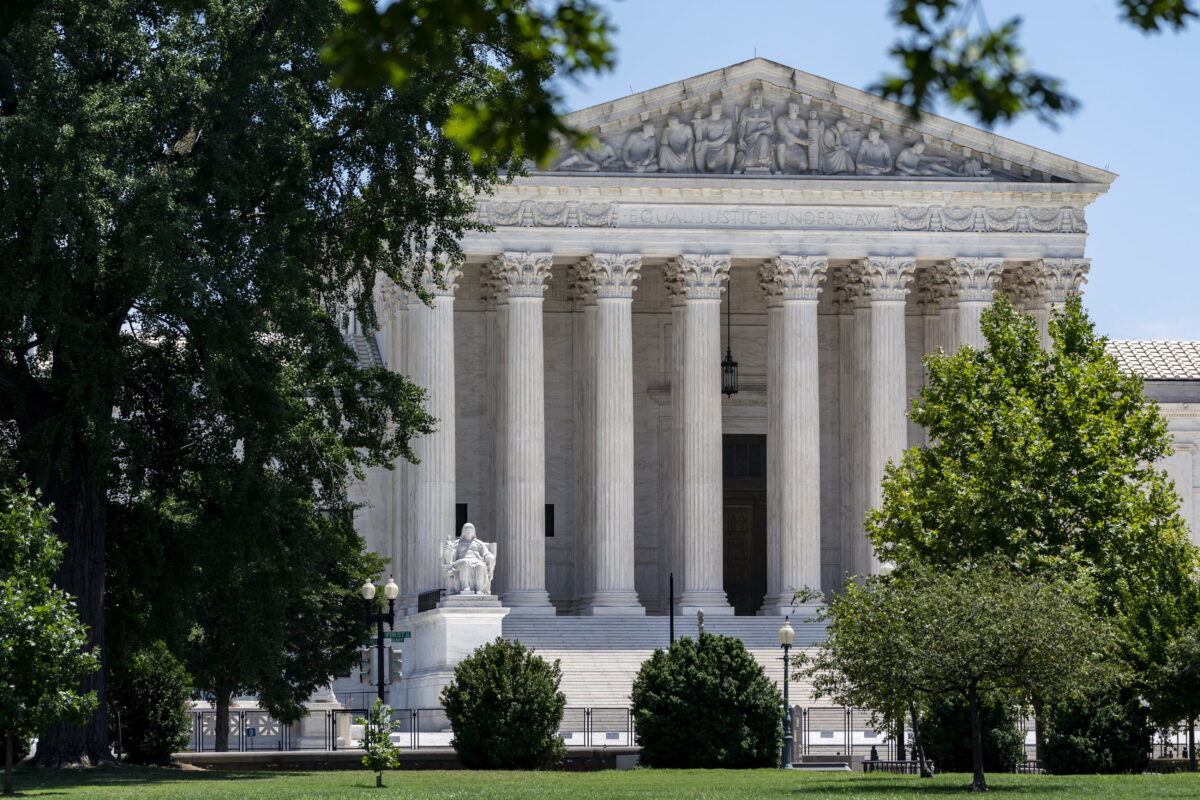
Supreme Court The Supreme Court is seen on Capitol Hill in Washington on July 14, 2022. (J. Scott Applewhite/AP Photo)

Incorrect Jury Instructions?

Katkin thinks U.S. District Judge Douglas Cole erred when he, in essence, instructed jurors that Sittenfeld violated the law if he accepted funds from “developers” who could benefit from that “some way, somehow.”

However, Katkin thinks it’s unlikely that Cole will rule that he was mistaken. Therefore, Katkin said, Sittenfeld will probably need to appeal to a higher court to rule on whether the jury instructions conflicted with the U.S. Supreme Court’s rulings in corruption cases.

At age 27, Sittenfeld had become the city’s youngest-ever councilman; he took office in 2011 and served until 2020, when he was suspended in the wake of his indictment.

Sittenfeld’s supporters, decrying “false and unjust allegations” against him, established a webpage called “Friends of PG Legal Support Effort.” They wrote: “We have absolute faith in PG’s character, his honesty, his ethics, his commitment to public service, and his love of Cincinnati, which he has served with excellence for a decade.”

Sittenfeld was one of three Cincinnati council members to face corruption charges in separate scandals in 2020.

Former councilwoman Tamaya Dennard, who pleaded guilty to taking $15,000 in bribes, was recently released from prison and has been working for a nonprofit that helps find employment for ex-convicts, according to The Cincinnati Enquirer.

No trial date has been set for another former Cincinnati councilman, Jeff Pastor.

Categories
Saved Web Pages

The FBI: A history of the capitalist rulers’ political police

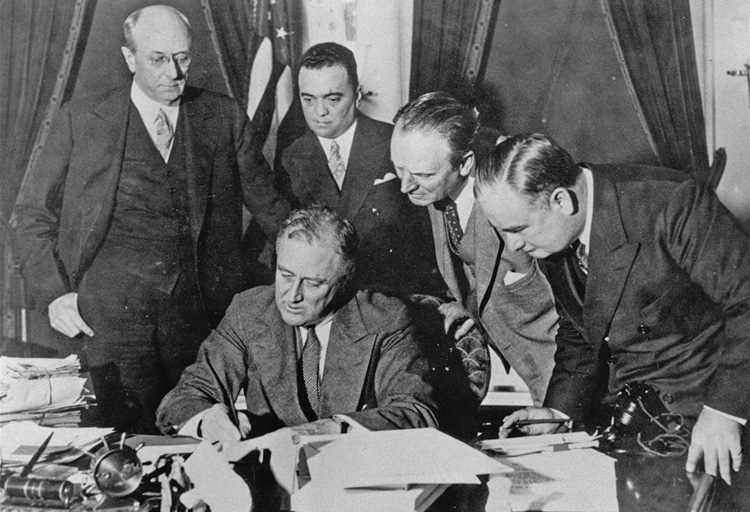
Democrat President Franklin Roosevelt, with FBI Director J. Edgar Hoover, to right of flag, signs 1934 bill increasing federal police powers for use against the labor movement. AP PhotoDemocrat President Franklin Roosevelt, with FBI Director J. Edgar Hoover, to right of flag, signs 1934 bill increasing federal police powers for use against the labor movement.

The Spanish-language edition of 50 Years of Covert Operations in the US: Washington’s Political Police and the American Working Class by Larry Seigle, Farrell Dobbs and Steve Clark, is one of Pathfinder’s Books of the Month for October. It traces the capitalist rulers’ use of Washington’s political police to target the unions and other working-class organizations, as well as mass movements for Black equality and against the Vietnam War. Today the Democrats wield the FBI to go after former President Donald Trump and others, attacking constitutional freedoms vital for the working class. The excerpt is from the chapter “Origins of FBI Assault on Socialist Workers Party.” Copyright © 2014 by Pathfinder Press. Reprinted by permission. 

For several years after the First World War, the FBI had functioned as a political police force, carrying out the arrest or deportation of some 3,000 unionists and political activists in 1919 and 1920 (the infamous “Palmer Raids”). But following widespread protests over these and other FBI actions, and with the decline of the postwar labor radicalization, the capitalist rulers decided against a federal secret police agency. …

By the mid-1930s, however, a vast social movement was on the rise, with the Congress of Industrial Organizations (CIO) at the forefront. The relationship of forces was shifting in favor of working-class organizations. The bosses’ old methods could no longer always be counted on. Communist perspectives did not come close to commanding majority support among working people, and in fact remained the views of a small minority, but the bosses were nonetheless concerned that progressive anticapitalist and anti-imperialist political positions advanced by class-struggle-minded union leaders were winning a hearing among a substantial section of the ranks of labor. Especially in times of crisis, such as war, minority points of view defended by established and respected working-class fighters could rapidly gain support.

With this in mind, the administration of President Franklin Roosevelt expanded and centralized federal police power. …

[T]hese FBI operations began on the eve of the Second World War. They were central to preparations by the US capitalist rulers to lead the nation into another carnage to promote their interests against their imperialist rivals and against the peoples of Asia, Africa, and Latin America struggling for liberation from colonial domination. These operations were directed against the leadership — and potential leadership — of the two major social forces in the United States that threatened to interfere with the ability of the US ruling families to accomplish their objectives: the labor unions and the Black movement. …

The drive toward war necessitated an assault on working people at home and against democratic rights in general. Roosevelt gave FBI chief J. Edgar Hoover free rein to use the FBI against the labor movement and Black organizations. The White House and Justice Department secretly authorized many of the illegal methods used by the FBI and turned a blind eye toward others.

This authorization for the FBI to assume the functions of a political police force was done without legislation, which would have had to be proposed and debated in Congress. It was accomplished instead by “executive order,” a device that was rapidly assuming a major place in the operations of the government and would increasingly become a major mode of governing in the decades to come.

On September 6, 1939, Roosevelt issued an executive order directing the FBI “to take charge of investigative work” in matters relating to “espionage, counterespionage, sabotage, subversive activities and violations of the neutrality laws.” The key phrase was “subversive activities,” and the most important decision was to include this slippery concept in the list of responsibilities given the FBI. While there were federal laws against espionage, sabotage, and violation of US “neutrality,” no law explained what “subversive activity” might consist of.

Two days later Roosevelt — again by executive decree — made a “finding” of the existence of a “national emergency.” This allowed an increase in military spending without having to ask Congress… . Simultaneously, the president ordered an expansion of the FBI’s forces. His objective, Roosevelt told a news conference, was to avoid a repetition of “some of the things that happened” during World War I:

There was sabotage; there was a great deal of propaganda by both belligerents, and a good many definite plans laid in this country by foreign governments to try to sway American public opinion. … It is to guard against that, and against the spread by any foreign nation of propaganda in this country which would tend to be subversive — I believe that is the word — of our form of government.

Forty years later, in a Foley Square courtroom in New York City, top Justice Department officials would cite Roosevelt’s words as providing legal authority — derived from the president’s “inherent powers” under the US Constitution — for the FBI’s campaign of spying, disruption, and provocation against the Black movement, unions, and antiwar and women’s liberation fighters and against communist organizations such as the Socialist Workers Party and Young Socialist Alliance.

As the trial of the SWP lawsuit unfolded during the spring of 1981 in Judge Griesa’s courtroom, it became increasingly clear that the case revolved around issues far deeper than particular FBI abuses. The historical evolution of the FBI is part of a broader phenomenon in the United States. Underlying the threat today to the rights of privacy and freedom of association is the arbitrary rule by an expanding federal executive power. This power carries out policies at home and abroad that it is less and less able to openly proclaim or mobilize majority support for. It relies increasingly on covert methods to accomplish hidden or half-hidden objectives. …

[A]dvocating ideas and taking actions that are not illegal — even as defined by reactionary legislation — but are nonetheless considered inimical to the interests of those in power can make you the target of the political police.

Categories
Saved Web Pages

READ IT: FBI’s Brutal Draft Letter Firing Disgraced Agent Peter Strzok Revealed

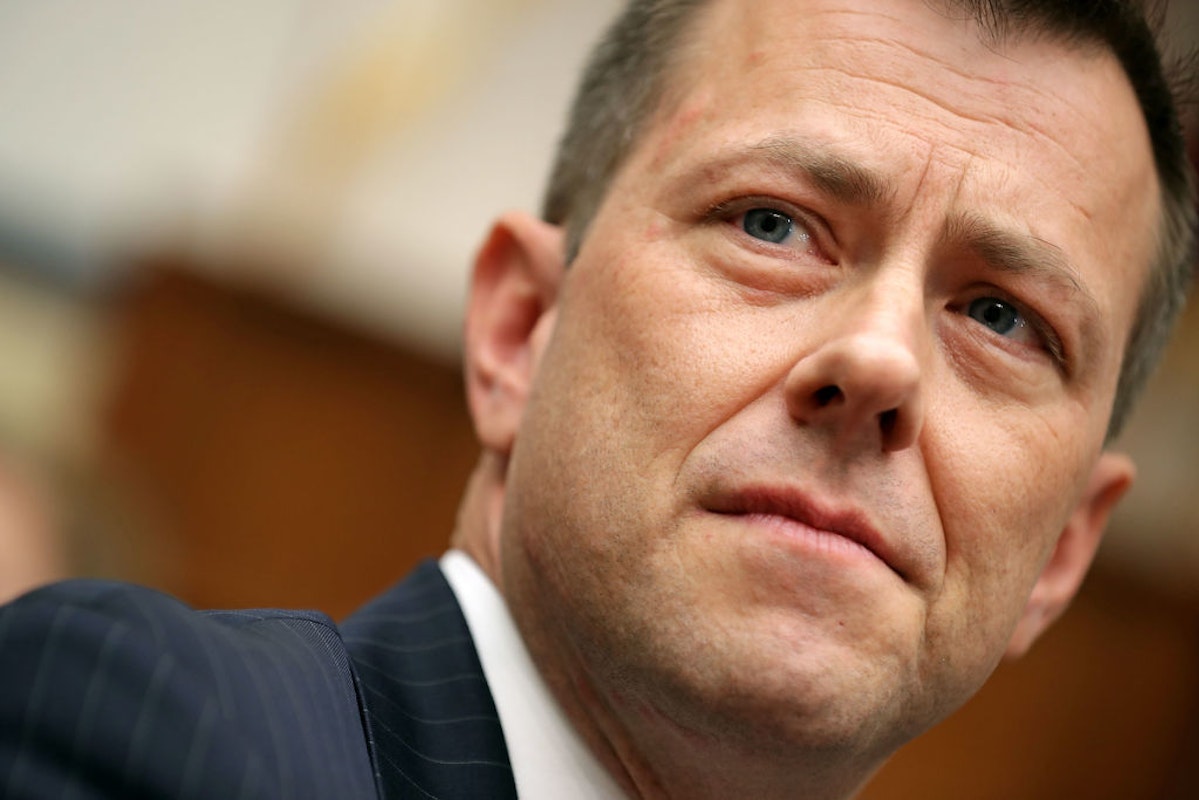
Peter-Strzok-1.jpg?w=1200&h=800&ixlib=re

A top FBI official accused Trump-hating former agent Peter Strzok of doing long-term damage to the bureau’s reputation with a “sustained pattern of bad judgment” and “selfishness” in the newly released draft of the 2018 letter firing him.

David Bowdich, who was deputy director of the bureau when he penned the brutally harsh draft of the dismissal letter, told Strzok the damage he caused to the bureau would last for years. He referred specifically to Strzok’s use of “an FBI device,” an apparent reference to the shocking text messages sent on bureau cell phones between Strzok and his paramour, Lisa Page, in which vowed to stop former President Trump from being elected in 2016.

“While there is no doubt your 21 years of service to the organization cannot and should not be erased, it is difficult to fathom the repeated, sustained errors of judgment you made while serving as the lead agent in two of the most high profile investigations in the country,” Bowdich wrote in the August 8, 2018 letter. “Though the Office of the Inspector General found no evidence of bias impacted any of your or the FBI’s investigative actions or decisions, your sustained pattern of bad judgment in the use of an FBI device has called into question for many of the decisions made during both the Clinton e-mail investigation and the initial states of the Russian Collusion investigation.”

“In short, your repeated selfishness has called into question the credibility of the entire FBI.”

Strzok’s dismissal letter was published today:

“In my 23 years in the FBI, I have not seen a more impactful series of missteps that has called into question the entire organization and more thoroughly damaged the FBI’s reputation.”

h/t @walkafyre pic.twitter.com/rFILnxDL84

— Hans Mahncke (@HansMahncke) September 30, 2022

The draft letter was an attachment in a DOJ response in Strzok’s wide-ranging federal lawsuit alleging violation of his right to privacy and wrongful termination. Strzok’s attorneys deposed Bowdich and are now trying to depose Trump and FBI Director Christopher Wray in a bid to show his firing was political. The DOJ attached the draft letter to rebut the idea that Strzok’s firing was for political reasons.

Bowdich has since left the bureau and is vice president of global security for Disney. Strzok, despite being humiliated by the exposure of his emails, extramarital affair, and repeated bungling of investigations, has written a book and frequently appears on hard-left cable news channel MSNBC to defend the FBI against accusations of political bias.

Strzok served as deputy assistant director of the bureau’s counterintelligence division, leading the investigation into phony Trump-Russia collusion claims and before that, the probe of Hillary Clinton’s illegal use of a personal email server to send and receive classified documents.

Strzok was first fired from Special Counsel Robert Mueller’s team and then from the bureau after the Department of Justice’s inspector general in 2017 turned up the damning emails exchanged between him and Page. In them, the pair expressed contempt for Trump and his supporters and Strzok hinted at plans to derail his campaign.

Bowdich claimed Inspector General Michael Horowitz found no evidence that political bias affected FBI investigations involving Strzok, but said the public perception was otherwise.

“In my 23 years in the FBI, I have not seen a more impactful series of missteps which called into question the entire organization and more thoroughly damaged the reputation of the organization,” wrote Bowdich. “In our role as FBI employees we sometimes make unpopular decisions, but the public should be able to examine our work and not have to question motives.”

The two-page letter ends with a blistering reference to Strzok’s failure as a public servant.

“As Deputy Assistant Director, you were expected to be a leader who was beyond reproach and set an example for not only our direct subordinates, but others throughout the organization who watched and observed your behaviors and actions,” Bowdich wrote. “You failed to do so repeatedly and put your own interests [above] the interests of the organization. Though it pains me to do so, it is for this reason that I am dismissing you from the rolls of the FBI.”

In addition to the texts ending Strzok’s career, they appear to have wrecked his personal life. In one exchange the DOJ revealed in response to Strzok’s wrongful termination suit, the pair discuss Strzok’s wife seeing their correspondence.

“My wife has my phone,” Strzok wrote.

“Your wife left me a VM,” Page replied. “Am I supposed to respond? She thinks we’re having an affair. Should I call and correct her understanding? Leave this to you to address?”

“I don’t know,” Strzok wrote. “I said we were close friends and nothing more. She knows I sent you flowers. I said you were having a tough week.”

Categories
Saved Web Pages

Russian Cyberwarfare: Unpacking the Kremlin’s Capabilities

Russia-Tech-4.jpg

Even before Russian troops invaded Ukraine in February, many experts in the West, in Ukraine, and in Russia believed Moscow would use cyberattacks to inflict major damage on Ukraine prior to or after the start of the military offensive. Indeed, Russia has extensive and formidable cyber capabilities. Reality, however, has played out differently.

Exactly why cyber has not been a consequential front in Russia’s invasion of Ukraine is unknown. It may be that Ukrainian cyberspace proved to be much better protected than some thought. Or it may be that Russia did not use its offensive cyber capabilities because the Kremlin interfered in every aspect of the preparation of the war, from military planning to cyber activities. The Kremlin wanted the invasion to play out as a “special operation” (in the Kremlin’s words), not a conventional military offensive. In this, as in much else, the Kremlin greatly miscalculated.

While an answer to the mystery of Russian cyber successes and failures in and around Ukraine is beyond the scope of this report, the case is nonetheless instructive, underlining the importance of understanding how Russian cyber operations are governed. The political element has always been decisive in the Russian cyber playbook, much more so than in other parts of the Russian security state. It, thus, comes as no surprise that over the years the command-and-control structure managing Russian cyber operations has developed into something very different.

The list of Russian cyber actors is long and complicated. It includes private entities, both legitimate and criminal, alongside traditional security services, the military, and the top political level where decisions are made. The relationship among these actors has changed quite significantly in the past six years. This report is an attempt to map the Russian cyber landscape and to help understand the intricate web of cyber actors.

Key Russian cyber actors include:

  • The FSB: The Federal Security Service (Federalnaya Sluzhba Bezopasnosti; FSB) is a major domestic security and intelligence agency. In cyber, the FSB’s capabilities are divided between those the agency has been building since the late 1990s (the 18th Center, or Information Security Center) and the capabilities the FSB acquired in 2003 when it absorbed several departments of the Russian electronic intelligence (ELINT) agency, the Federal Agency for Government Communications and Information, or FAPSI (the 16th Center of the FSB or the Center of Electronic Intelligence in Communications).
  • The SVR: The Foreign Intelligence Service (Sluzhba Vneshney Razvedki; SVR) is Russia’s spy agency, a direct successor to the foreign intelligence branch of the KGB. The agency never went through any structural reforms, but its capabilities were significantly expanded in the 2010s, including in cyber.
  • The military: The cyber capabilities in Russia’s military are run by two directorates within Russia’s General Staff: the GU (or the Main Intelligence Directorate and the 8th These two directorates run operations and supervise Russian cyber troops and the military research and development effort. Cyber command was never launched despite several attempts in the early 2010s.
  • The Presidential Administration: The direct successor to the Central Committee of the Communist Party, the Presidential Administration supervises Russia’s intelligence and security services. An integral part of the administration is Russia’s Security Council, which provides strategic thinking in all areas of national security, including cyber; it is also a government body tasked with maintaining contact with its Western counterparts, including a cyber “red line” between Moscow and Washington.
  • Private cybersecurity companies: These companies are tied into Russia’s cyber effort via networks of official and unofficial contacts. Their role is to provide expertise and help with recruitment efforts.

Despite this broad range of actors involved in cyber operations on various fronts, Russia doesn’t have a unified cyber command. Rather, coordination with the political decision-makers is done at the Presidential Administration level, with Russia’s Security Council an integral part of the process. Moreover, unlike in the conventional field of operations, there is no strict division of labor between the agencies in the cyber domain. Agencies traditionally focused on foreign targets have attacked domestic targets (including nongovernmental organizations, journalists, and the Russian opposition). Outside Russia, the military has targeted political and private industry and the SVR and FSB have attacked military targets, and vice versa.

While reliable data are limited, this report delves deeply into the history and evolution of Russia’s cyber actors, revealing a remarkably fluid and informal landscape, which is often difficult to interpret and navigate even for those who operate within it. What emerges is a system of cyber operations that is:

  • Coordinated through a set of political processes centered on the Presidential Administration and the Security Council, rather than a traditional, military-style command structure;
  • Characterized by significant overlap in mission and capability, often leading to competition for resources and sometimes to problems of coordination and conflict;
  • Subject to a significant degree of informality and political maneuvering, as different actors report to the Presidential Administration and Security Council via different channels and with differing degrees of accountability; and
  • Heavily dependent on the private sector for training, recruitment, and technology, leading to a high degree of informal interagency integration at the grassroots level.

The United States and Russia have clashed for years over what terminology to use: “information security,” promoted by Russian officials, versus cyber, used by the United States. The Russian approach is more expansive and includes both psychological and technical elements, but essentially what the Kremlin means is control over online content — i.e., censorship.

Photo: Moscow, Russia. 2 November 2018. Russian President Vladimir Putin addresses a gala event to mark the centenary of the Main Directorate of the General Staff of the Armed Forces of Russia known as the GRU at the Russian Army Theatre Credit: Planetpix/Alamy Live News

Photo: Moscow, Russia. 2 November 2018. Russian President Vladimir Putin addresses a gala event to mark the centenary of the Main Directorate of the General Staff of the Armed Forces of Russia known as the GRU at the Russian Army Theatre Credit: Planetpix/Alamy Live News

2. History & Development

2.1. Origins

Today’s cyber command-and-control systems originated in the Soviet Union’s signals intelligence (SIGINT) bureaucracy.

Throughout the Soviet period, two intelligence agencies were involved in breaking codes. The KGB had the 16th Directorate, in charge of intercepting and deciphering foreign communications. The General Staff of Armed Forces had the 8th Directorate and the Special Service of the GRU. Two agencies together ran Soviet SIGINT (which did not intercept text or speech but focused on identifying radio signals) and ELINT (which intercepted text and speech, i.e., content) centers abroad, including a facility at Lourdes in Cuba, which monitored and intercepted radio communications in the United States. 1

Soviet military codebreakers were trained at the Krasnodar Higher Military School named after General of the Army S. M. Shtemenko — the school was supervised by the 8th Directorate of the General Staff. 2  The personnel for the 16th Directorate of the KGB were taught at the KGB Higher School, the Fourth (Technical Department) in Moscow. The Fourth Department of the KGB Higher School had a better reputation and attracted students from three Soviet agencies that sent their recruits to study cryptography: the KGB, the Ministry of Defense, and the Ministry of Radioelectronic Production.

The KGB and GRU actively recruited talent in civilian universities known for their excellent math programs — the Moscow State University’s departments of Physics and Math and Mechanics and Math (the latter had helped to form the Fourth Department of the KGB Higher School), Moscow Engineering Physics Institute (MEPhI), and Moscow Institute of Physics and Technology (MFTI or PhysTech).

This system largely survived the collapse of the Soviet Union.

Timeline 1

2.2. The 1990s: The FAPSI Monopoly and Connection to the Cyber Industry

The KGB was restructured when the Soviet Union dissolved in late 1991. The 16th Directorate, along with several departments in charge of providing secure communications for party bosses, became the Committee of Government Communication. In December 1991, it was renamed as the FAPSI. 3  The idea was to create a Russian analogue of the US National Security Agency (NSA), but the FAPSI was also entrusted with conducting public opinion polls — for the Kremlin’s eyes only — and, later on, with providing digital security for Russian elections.

The system of training and recruitment remained the same — the Fourth Department of the KGB Higher School, which was renamed as the Institute of Cryptography, Telecommunications and Computer Science (IKSI) within the FAPSI, and the FAPSI kept recruiting at MEPhI, MFTI, and Moscow State University. In 1996, the FAPSI sponsored the establishment of the Educational and Methodological Association of Higher Educational Institutions on Information Security (UMO IB) under the auspices of the IKSI.

The FAPSI was structured into six main directorates. The most important was the 3rd Directorate — the Main Directorate of Electronic Intelligence in Communications (Glavnoye Upravlenie Radioelectronnoi Razvedki Na Setyah Svyazi; GURRSS), in charge of spying on foreign telecommunications. The 3rd Directorate was the former 16th Directorate of the KGB.

Between 1995 and 1998, the 3rd Directorate was led by Vladislav Sherstyuk, a KGB officer since 1966 and a graduate of the Physics Department at Moscow State University. Sherstyuk would play a major role in Russia’s approach to cyber issues for decades.

Sherstyuk saw military action in the First Chechen War — he was put in charge of the FAPSI’s task group deployed to Chechnya, and he organized the interception of the Chechens’ communications.

In 1998, Sherstyuk was named head of the FAPSI. 4  The same year the FSB — the major domestic counterintelligence and counterterrorism agency — under the leadership of a new director, Vladimir Putin, entered the cyber field. In the Central Apparatus of the FSB, a new unit called the Directorate of Computer and Information Security (UKIB – Upravlenie Kompyuternoy I Informatsionnoy Bezopasnosti) was formed. It was subordinate to a larger department of counterintelligence. The UKIB was housed in a blockish, looming structure that was once the KGB’s Computation Center, on the corner of Lubyanka Square and Myasnitskaya Street in Moscow. The FAPSI was headquartered in a stark, modern terraced building with giant antenna globes on the roof not far from Lubyanka Square, on Bolshoy Kiselny Lane.

In the Armed Forces, the General Staff’s 8th Directorate was still operational, but it lacked resources. Both the FSB and the military’s cyber capabilities were largely overshadowed by the FAPSI.

The early 1990s also saw the emergence of private cyber companies, like Kaspersky Lab, where the management had worked for the KGB. Kaspersky Lab CEO Evgeny Kaspersky himself had graduated from the Fourth Department of the KGB Higher School. 5  Thanks to their KGB background, those companies cultivated close relations with the security services and law enforcement agencies. What helped the FAPSI cultivate those relationships was that over the years the agency had been creating an industrial empire engaged in information security. The FAPSI was also in charge of licensing information security software — firewalls, cryptography, and so on — which meant that private companies needed to cooperate with it to get licenses. 6

The period from 1998 to 1999 was probably the most influential time for the FAPSI.

In May 1999, Sherstyuk was transferred to the Security Council as its first deputy head. In December, he was appointed to preside over the information security section. 7  That section became the main unit where the cyber and information security concepts were implemented. One of the brains behind it was Anatoly Streltsov, a former KGB colonel.

Both Sherstyuk and Streltsov understood that they needed a research facility on cyber political issues that would help them engage in political decision-making on cyber. Thus, a department was created within Moscow State University under Sherstyuk and Streltsov’s supervision which soon became the Institute for Information Security Issues. This institute emerged as a major think tank that defines Russian foreign policy on information security.

In 2000, Sherstyuk and Streltsov’s team composed the “Doctrine of the Information Security of the Russian Federation,” which included a broad list of threats, ranging from “compromising of keys and cryptographic protection of information” to “devaluation of spiritual values,” “reduction of spiritual, moral and creative potential of the Russian population,” as well as “manipulation of information (disinformation, concealment, or misrepresentation).” 8

Throughout the 1990s, the FAPSI and officials affiliated with it controlled the Russian cyber domain by training, conducting operations, co-opting the private cyber industry, and establishing government cyber policies.

Timeline 2

2.3. The 2000s: The FSB Takes Over

2.3.1. Structural changes

The early 2000s saw a massive and rapid expansion of the FSB, including into the cyber arena.

On March 11, 2003, President Putin split the FAPSI between the FSB, the SVR, and the Federal Protective Service (FSO), in charge of providing protection for him and other high-level officials.  9

Government communications and polling of public opinion were considered such a sensitive domain they were given to the FSO to supervise — and within that agency, the Service of Special Communication and Information (Sluzhba Specialnoy Svazyi I Informatsii; SSSI). The 3rd Directorate was moved to the FSB and became the 16th Center of the FSB (the Center of Electronic Intelligence in Communications). The regional ELINT units of the FAPSI were reorganized into the FSB Information Reception Centers.

In 2004, the FSB underwent administrative reform just like the rest of the federal agencies. Departments were renamed as services, and the UKIB was turned into the Information Security Center (TsIB or Centr Informatsionnoy Bezopasnosti) or the 18th Center of the FSB. The new center remained within the Service of Counterintelligence.

The FSB was divided into two large parts. The operations departments carried out counterintelligence, intelligence, counterterrorism, and other activities, whereas the support side of the organization included such activities as creating and providing special technical equipment and meeting other material needs. The TsIB was situated in the operations department, which was the most proactive. It was involved not only in the technical protection of computer networks but also in active operational surveillance, clandestine activity, and intelligence collection on the Internet. Inside the TsIB, the Operative Directorate was created to conduct operations.

The SVR founded a scientific production center, Delta, to conduct research and development (R&D) on cyber issues.  10 Delta was subordinate to the Directorate of Informatization of the SVR.

2.3.2. Cyber policymaking

Sherstyuk continued to define cyber policy while at the Security Council, the central body at the Presidential Administration responsible for managing the formulation and execution of security-related policies, though his position changed. In 2004, he was demoted to the position of assistant to the head of the Security Council. He was forced to rely on the FSB’s support since the most important departments of his former agency had been incorporated into the FSB. He also ensured the continued existence of the Institute for Information Security Issues at Moscow State University.

At the Foreign Ministry, Sherstyuk’s team was supported by Andrei Krutskikh, an arms control talks veteran who shared Sherstyuk’s approach to cyber issues detailed in the “Doctrine of the Information Security of the Russian Federation.”  11

The General Staff was sidelined by the FSB, which, for the most part of the 2000s, successfully rebuffed all attempts by the military to expand into the area of cyber.

2.3.4. Modus operandi under development

The 2000s were the period when the first cyberattacks took place beyond Russia’s borders, including an attack on Estonia in 2007. Proxy groups affiliated with the Presidential Administration took responsibility for these attacks. APT29 or Cozy Bear — a Russian hacker group believed by Western cyber experts to be affiliated with either the FSB or SVR — was operational since at least 2008, according to Western experts.

2.3.5. Recruitment and training

The former FAPSI directorates, now within the FSB, continued recruiting from MEPhI, MFTI, and the Physics and Math Department at Moscow State University.

In training, the IKSI, previously within the FAPSI, was placed under the control of the FSB and became part of the FSB Academy.

The national program of training of civilian rank and file was significantly expanded: 73 Russian universities and high schools came to teach information security, united in the UMO IB. The chief institution supervising the association was the IKSI, which defined the UMO IB’s requirements and guidelines. Of the 73 universities and high schools, only five institutions were military; the rest were higher polytechnic schools and state universities across the country.

Training in cyber followed the Soviet model of prioritizing loyalty and technical prowess over ethical considerations, resulting in an effective and devoted cyber workforce. After being recruited, students rarely, if ever, questioned why they were tasked with attacking Western or domestic targets, including Russian journalists and opposition politicians. Once again, the Soviet legacy is to blame. The Soviet Union had the biggest engineering community in the world because of its huge military-industrial complex — a collection of industries and research facilities which worked exclusively for the Soviet army and the KGB. To serve it, Josef Stalin founded dozens of technical schools all over the country. For many decades, Soviet engineers were schooled intensively in technical subjects but rarely had exposure to the humanities. The scope of their education was exceedingly narrow. Unlike medical doctors who were trained in ethics, engineers were not. They were taught to be technical servants of the state. They were also taught secrecy since most of them were meant to work for the military-industrial complex of the KGB. As a result, generations of engineers were trained and worked their entire lives with little understanding of politics or trust of politicians and were suspicious of public activity as a whole. That system was never reformed after the collapse of the Soviet Union. After Putin became president, the Soviet approach to technical education based on secrecy and patriotism was only reaffirmed.

In addition, Russia’s security services adopted a new tactic: approaching Russian criminal hackers and recruiting them. The FSB found itself in a good spot because the TsIB was tasked to prosecute criminal hackers. Thus, they were able to give the hackers a choice: either join the FSB or go to prison. Of course, some accepted and even joined the TsIB. 12  The 2008 Russia-Georgia war only helped to solidify this new approach, but there are reports that some Russian hackers had been recruited even before the war. 13

In 2009, the Education Ministry introduced a new educational standard that institutionalized “information security” as an area of study in Russian universities — cyber became a national priority in Russia’s higher education. 14 

Timeline 3

2.4. The 2010s: Explosive Growth

2.4.1. Structural changes

In 2012, Sergei Shoigu was appointed minister of defense. Ambitious and energetic, Shoigu wanted to prove himself as a military expansionist — cyber was a promising domain for increasing military influence. He also wanted his own cyber troops. He correctly identified the potential source of cyber personnel: the country’s extensive network of technical universities.

In July 2013, Shoigu attended a meeting with Russian rectors at the Moscow State Technical University (MGTU) (one of the 73 educational institutions that provided training in information security) and told them of “a start of a major hunt for young programmers.” 15  Later that same year, Russia’s cyber troops were launched and advertised on YouTube, with the Kalashnikov rifle compared to a laptop. 16

The Russian army still largely relied on the draft, and Shoigu tightened the rules for conscripts. It became impossible to avoid military service after graduating from college. When the cyber troops were launched, students in polytechnic universities were presented with a choice: either go to some distant army unit in Siberia or join the cyber troops, where students were used to staff the so-called research companies (military units). The first “research company” was launched at the Military Airforce Academy in Voronezh – one of the five military schools on the list of 73 universities that were providing training in information security.

By 2014, the list of Russian universities teaching information security had expanded to 170. 17

The Russian army skillfully exploited an old, outdated mechanism of draft to recruit the best and brightest among the Russian technical intelligentsia, sidelining the FSB. In the military, training in information security is supervised by the 8th Directorate of the General Staff in coordination with the Military Education Department of the Main Personnel Directorate of the General Staff.

The military also used other recruitment methods developed by the FSB — in 2015, the Capture the Flag (CTF) competitions run by the Association of Chief Information Security Officers (ARSIB, or Assotsiatsiya Rukovoditeley Sluzhb Informatsionnoy Bezopasnosti) got a new sponsor, the Special Development Center of the Ministry of Defense. 18  That center was launched by the Ministry of Defense in 2014 as a leading military cyber facility. 19  That same year, in December 2014, the 8th Directorate of the General Staff founded a research center on information security within the Krasnodar Higher Military School named after General of the Army S. M. Shtemenko. 20  One of the “research companies” was based at the center and supervised by the 8th Directorate and the Science-Technical Committee of the General Staff — the main customers of R&D in the military. 21

2.4.2. Cyber policymaking

The old guard led by Sherstyuk and Krutskikh still controlled Russia’s cyber policy domain, but new actors came into play. First, the FSB delegated the head of the Science-Technical Service (NTS), Nikolai Klimashin, to the Security Council. He replaced Sherstyuk who remained active through his position at the Institute for Information Security Issues at Moscow State University. Klimashin did not have a background at the FAPSI, but he was chosen to supervise the liquidation and absorption of the FAPSI in 2003 (Putin wanted to have just one major intelligence/security agency — the FSB — not a competition of several agencies which his predecessor, Boris Yeltsin, had encouraged). As a result, Klimashin’s NTS now included a department of the absorbed FAPSI, the Main Directorate of Security of Communications (GUPS), which became the 8th Center of the FSB or “the Center for Information Protection and Special Communications.”

The General Staff of the Armed Forces became engaged in the cyber policy debate. One of the leading military cyber experts was Sergey Komov, himself a product of military SIGINT training (Komov attended Kyiv’s military radio-technical school and Govorov’s military radio-technical academy in Kharkiv).

Since the early 2000s, Infoforum, a major Russian cyber conference, has been held in Moscow and later in the other regions. The General Staff has made sure to attend every Infoforum conference since 2013. As a rule, the head or deputy head of the 8th Directorate of the General Staff has been in attendance, sometimes accompanied by the head of the Military Science Committee of the General Staff.

The year 2016 saw the highest point of attention to cyber from the Kremlin. In February 2016, the Infoforum conference opened with a speech by Sergei Ivanov, then the chief of the Presidential Administration. “The powerful potential of such authoritative discussion platforms as Infoforum is fully engaged in solving the issues of ensuring information security,” Ivanov said. Ivanov was a former general of the foreign intelligence branch of the KGB, a close associate of Putin’s, and served as minister of defense from 2001 to 2007. He was also reportedly one of the masterminds of the Russian interference in the US elections in 2016. 22

On August 12, 2016, Ivanov was removed from his position as chief of Putin’s administration (most likely because of the US outcry over the hacking of Democratic National Committee servers), but Putin preserved his seat on the Security Council.

Ever since, no Infoforum conference has been opened by the chief of Putin’s Presidential Administration. It is quite likely that Putin no longer wants a direct connection between the Kremlin and a public cyber event.

2.4.3. Development of recruitment techniques

In 2010, a collection of private cybersecurity companies launched the ARSIB. The ARSIB was led by Victor Minin, a former officer of the KGB and FAPSI. The ARSIB runs the CTF competition at schools and universities in Russia. CTF is a massive, multiday hackathon in which one team defends its server as another team attacks it. 23  Minin told the authors of this report that the CTF competitions were seen by Russia’s intelligence community as a perfect recruitment mechanism.

CEPA Forum 2022

Meeting the Moment: Allies at a Crossroads

Register Now

3. Russia’s Evolving Cyber Command

3.1. Russia’s Cyber Landscape after 2013

Throughout the turbulent period between 2013 and 2016, marked by Russia’s invasion of Ukraine and illegal annexation of Crimea in 2014 and reckless interference in the US elections two years later, Russian cyber actors went through a series of crises brought on by the Kremlin.

By and large, the traditional actors, foremost the FSB, maintained a dominant role since they were well entrenched in the Russian security bureaucracy, including in positions on the Security Council, the Presidential Administration, and the Foreign Ministry.

FSB

Inside the FSB, the TSiB and the 16th Center remained the two most important cyber players.

In information sharing and recruitment/training:

  • The TsIB was focused on using the connections between the vast Russian criminal hacking community and Russian private cybersecurity companies, including Kaspersky Lab. The FSB also made the TsIB a contact point with Western counterparts to share intelligence about Russian criminal hacker activity worldwide. The TsIB made amusingly good use of the shared intelligence. It tracked down Russian hackers and sought to recruit them. 24
  • The 16th Center relied on its significant cyber capabilities and recruited new talent in Russian polytechnic schools with courses in information security, supervised by the FSB’s IKSI.

The head of the 16th Center, Sergey Buravlyov, held the position of deputy director of the FSB since 2005, and in 2013 he was promoted to the Security Council as deputy secretary, replacing Klimashin. Buravlyov was part of Sherstyuk’s circle. Another one of Sherstyuk’s protégés, Krutskikh, who had been serving at the Foreign Ministry, got a new position. In February 2014, Putin appointed Krutskikh as his special representative for international negotiations on Internet regulation. 25

After the illegal annexation of Crimea in 2014, there was a significant and sudden increase in Russia’s military cyber capabilities.

The Russian army found a way to boost its capabilities both in human resources and expertise. Rank and file were provided via the skillful use of the draft — students in Russian polytechnic schools joined Russian cyber troops in droves. The army also expanded training in cyber at military schools that taught personnel for SIGINT units (in Russian terminology, radio technical intelligence, or OSNAS), like the Higher Military School of Radioelectronics in Krasnoyarsk.

Contracts were also granted to private cyber companies. In 2015, Kaspersky Lab’s software was chosen by the Ministry of Defense as its primary antivirus solution. “By supplying the Kaspersky Business Space Security to the Russian Ministry of Defense through partners, we marked the beginning of a very important cooperation for us,” said Sergey Zemkov, managing director of the Russian office of Kaspersky Lab at the time. 26

The interference in the 2016 US elections (APT29 and APT28) and the resulting backlash from the US intelligence community created a crisis in Moscow where officials blamed one another for getting caught. The TsIB was decimated as a result of purges. Two senior TsIB officers were arrested on charges of treason. The head of the investigations unit at Kaspersky Lab and the head of the TsIB were forced to resign. The head of the TsIB’s deputy also lost his job.

In January 2017, Buravlyov was quietly removed from the Security Council. Contrary to all Kremlin rules, no public announcement was made about his resignation. Buravlyov was replaced by Oleg Khramov, a brutal FSB general with no background in cyber but with experience conducting offensive operations in Ukraine. Apparently, both the TsIB and Buravlyov, who maintained officially sanctioned contacts with Western counterparts, fell victim to the Kremlin’s paranoia.

As a contact point with Western powers, the TsIB was replaced by the 8th Center of the FSB. A national computer emergency response team (CERT), called the National Coordination Center on Computer Incidents, was built in the 8th Center. The 8th Center also originated from the FAPSI, but it was part of the NTS of the FSB; thus, it was not on the operational but rather the support side of the FSB.

Of the two cyber actors within the FSB, the 16th Center (dubbed Berzerk Bear, Dragonfly, and Energetic Bear by Western cyber researchers) emerged as a primary cyber offensive unit. In 2021, US authorities accused three officers of the 16th Center of sending fake e-mails with infected attachments to energy, including nuclear, companies in the United States between 2012 and 2017. According to the indictment, the three officers used spearphishing attacks that targeted more than 3,300 users at more than 500 US and international companies. They also targeted US government agencies such as the Nuclear Regulatory Commission. 27 

Timeline 4

3.2. Military’s Cyber Activities

3.2.1. Further expansion of the military

In recent years, the Ministry of Defense has built grand new facilities, like the buildings of the Krasnodar Higher Military School named after General of the Army S. M. Shtemenko and the Elite of the Russian Army (ERA) Technopolis in the Krasnodar region, operational since 2018.

The ERA Technopolis houses eight “research companies,” including the “first research company” launched within the Military Airforce Academy in Voronezh — one of the five military schools on the original list of 73 educational institutions providing training in information security. The Advanced Research Projects Foundation (FPI), established in 2012 as a Russian analogue of the US Defense Advanced Research Projects Agency (DARPA), was also partly relocated to the ERA. 28

The Ministry of Defense also found a new use for the military research facilities not previously associated with cyber.

GRU

The Central Scientific Research Institute of Chemistry and Mechanics (TsNIIKhM) has been the major research institution in the Russian military-industrial complex since before the Russian Revolution of 1917, involved in development and production of gunpowder, ammunition, and explosives for the army (in the Soviet Union it was known as NII-6). In 2005, the TsNIIKhM was subordinated to the Federal Technical and Export Controls Service in charge of protecting state secrets from foreign intelligence services via technological means. “This decision was the reason for a radical restructuring of this work, including the organization of new areas of scientific research,” TsNIIKhM’s website declared. 29

On October 23, 2020, the US Department of the Treasury’s Office of Foreign Assets Control (OFAC) designated the TsNIIKhM, pursuant to Section 224(a)(1)(A) of the Countering America’s Adversaries Through Sanctions Act (CAATSA), for knowingly engaging in significant activities undermining cybersecurity against any person, including a democratic institution, or government on behalf of the Russian government. 30  The TsNIIKhM was found responsible for building a customized tool that enabled the August 2017 cyberattack on a Middle Eastern petrochemical facility. 31  The TsNIIKhM developed the Triton malware, also known as TRISIS and HatMan, to target and manipulate Industrial Controls Systems (ICS) that are used in some critical infrastructure facilities. The TsNIIKhM deployed the malware through phishing that targeted the petrochemical facility.

On the operations side, the 85th Main Special Service Center (Glavny Tsentr Specialnoy Sluzhbi; GTsSS), or military unit 26165 (dubbed Fancy Bear, APT28, or Strontium by Western cyber researchers) emerged as the main offensive facility of the Main [Intelligence] Directorate of the General Staff, along with military unit 74455. 32  In the Soviet Union, that center was part of the GRU’s radio technical intelligence, or SIGINT; it was updated in the 2000s.

The GTsSS has been recruiting new talent in Russian schools since at least 2014 via cooperation with the FSB’s IKSI. 33  It also recruits at hackers’ conventions (see below). At least one officer of that center, Aleksey Morenets (wanted by the FBI since 2018), graduated from the Military Airforce Academy in Voronezh. 34  There is also 18 TSNII (Central Research Facility), or military unit 11135, operational since 1938, which has been involved in SIGINT/ELINT research, including “developing the equipment for conducting and coding satellite reconnaissance activities,” and is now involved in information security under the auspices of the Main [Intelligence] Directorate.

The supervision of the cyber units in the military stayed the same — the 8th Directorate, the Main [Intelligence] Directorate, and the Science-Technical Committee, all at the General Staff of the Armed Forces.

3.2.2. Military setbacks

As early as March 2012, Russian Deputy Prime Minister Dmitry Rogozin spoke of the need to create a Russian military cyber command. 35  In February 2013, Shoigu announced his intention to create a cyber command and ordered the General Staff to provide him with recommendations. The defense minister set an end-of-2014 deadline. 36  However, the cyber command was never set up.

In 2017, Aleksander Sherin, deputy chair of the Duma’s Committee on Defense, denied the existence of a cyber command and cyber troops in Russia. 37

One of the reasons for this setback could be that the political decision-making in cyber is still dominated by the FSB (at the Security Council).
Photo: Director of Russian Federal Security Service (FSB) Alexander Bortnikov and Director of Foreign Intelligence Service (SVR) Mikhail Fradkov arrive for a wreath-laying ceremony marking the 75th anniversary of the Nazi German invasion, by the Kremlin walls in Moscow, Russia, June 22, 2016. Credit: REUTERS/Grigory Dukor

Photo: Director of Russian Federal Security Service (FSB) Alexander Bortnikov and Director of Foreign Intelligence Service (SVR) Mikhail Fradkov arrive for a wreath-laying ceremony marking the 75th anniversary of the Nazi German invasion, by the Kremlin walls in Moscow, Russia, June 22, 2016. Credit: REUTERS/Grigory Dukor

3.3. The Relationship between Russian Private and Security/Military Cyber Actors

Both the security services and the military have relied significantly on private actors to develop offensive cyber tools and conduct cyber operations.

Russian state/private partnership in cyber works in several ways.

3.3.1. Partial privatization of the networks of R&D facilities inherited from the KGB

Russian security agencies and the military rely on an empire of research institutions they had built in Soviet times. In the Soviet Union, a significant effort was made to hide and disguise the true affiliation of these research institutions. Take, for example, the Scientific Research Institute of Dalny Svyazi, or of long-distance communications, in St. Petersburg, known as Dalsvyaz. The institute, with a staff of more than 10,000, was overseen by the Ministry for Industrial Telecommunications, but its real purpose was to work for the military. The offices of the applied acoustics unit (working on voice and speaker recognition) of Dalsvyaz were always guarded by men with automatic weapons because the unit was not under the control of the institute at all but was instead run by the KGB. It was a classic Russian matryoshka — secrets within secrets. 38

Many of those research centers survived the collapse of the Soviet Union, like the Kvant Scientific Research Institute, founded in 1978 as a laboratory within the Design Bureau of Industrial Automation of the Ministry of Radio Industry. The ministry was officially civilian, but the Design Bureau of Industrial Automation was part of the Soviet military-industrial complex, while the Kvant laboratory was under the KGB. Kvant developed computers for the 16th Directorate of the KGB. It remained under control of the FAPSI in the 1990s and went to the FSB in the 2000s. At present, Kvant develops cyber weapons for the 16th Center of the FSB, essentially the same organization the institute has been working for since the beginning. The Design Bureau of Industrial Automation also remains active — now it’s part of the Rostech empire and involved in developing drones.  39

What has changed is that Kvant has launched private entities to work on FSB contracts. One of them is SyTech, a small company which has worked on contracts for the 16th Center since 2009, including a project for collecting data about users of social media (such as Facebook, MySpace, and LinkedIn), a project for deanonymizing Tor traffic with the help of rogue Tor servers, and a project to covertly penetrate P2P networks, like the one used for torrents. 40  On the surface, SyTech is a private company, but it shares personnel and contracts with Kvant (under US sanctions since June 11, 2018). 41

This same approach is being used by the SVR. The agency has worked with private entities like AO Pasit, affiliated with the SVR, on SVR contracts using its scientific production center “Delta” as a customer. 42

SVR

3.3.2. The role of private cybersecurity companies in recruitment and developing tools

The Russian company Positive Technologies identifies vulnerabilities in networks and publishes highly regarded research. 43  In April 2021, the company was blacklisted by the US Treasury for supporting the FSB. 44  According to the US Treasury, “Positive Technologies provides computer network security solutions to Russian businesses, foreign governments, and international companies and hosts large-scale conventions that are used as recruiting events for the FSB and GRU.” The company said these were “groundless accusations,” while its chief operating officer, Maxim Pustovoy, said the blacklisting was based on “a misunderstanding and a mistake.” 45  Positive Technologies has organized hacker competitions — Positive Hack Days and The Standoff — since 2011. 46  These events have been organized very much like the ARSIB’s CTF competitions, used by the FSB to approach and recruit young talent (Kaspersky Lab also sponsored Positive Hack Days). 47  An officer of the 85th Main Special Service Center (military unit 26165) of the Russian military intelligence — Dmitriy Badin (wanted by the FBI since 2018) — took part in Positive Hack Days in 2014. 48  The same conference was also attended by officers of the FSB. 49

Senior managers of Positive Technologies attended Infoforum conferences since at least 2013 and spoke alongside Krutskikh and officers of the FSB. Since 2014, Positive Technologies has sponsored Infoforums. 50

Another Russian company, also blacklisted by the US Treasury, is Digital Security, a cyber research group. According to the US Treasury, “Digital Security worked on a project that would increase Russia’s offensive cyber capabilities for the Russian Intelligence Services, to include the FSB.” 41

What Positive Technologies and Digital Security have in common is that their business is identifying vulnerabilities in networks. Digital Security, however, has also held a competition/conference for white hat hackers, called ZeroNights, since 2011. 51  So those companies not only develop tools for Russian security services but also provide them with recruiting opportunities.

Digital Security’s founder, Ilya Davidovich Medvedovsky, also co-wrote a book, Attack on the Internet, with two others, including a leading professor of information security at Peter the Great St. Petersburg Polytechnic University. 52

3.3.3. The challenge of linking cyberattacks to the SVR

The SVR is an ambitious and capable intelligence-gathering agency. For several years, Western cyber experts attributed cyberattacks on Western targets to the SVR (in particular, the attacks carried out by APT29). However, unlike other Russian agencies, such as the FSB and GRU, where attribution was verified independently by Russian and Western investigative journalists, no details that would help link cyberattacks to a particular unit at the SVR or expose the chain of command inside the agency were ever found.

A real-life story: a Russian hacker’s career in the year 2020

A young man in his early 20s, originally from an eastern suburb of Moscow, was a student at Bauman Moscow State Technical University. His father, a trained engineer, was a manager in a small private company, and his mother was an accountant. The young man was about to be conscripted to the army — a problem which all young men faced in Russia. Since the student studied computer science and information systems at the university — much like many other students — he was given a choice: either serve a year in a military unit located far from Moscow and live in the barracks; or join the cyber troops, stay in Moscow, share a room with another student, and visit family every weekend. A small salary for his service was also included. The young man did not hesitate. He decided to join the cyber troops, as did many of his peers, and stayed in Moscow. When he had finished his time in the army, the FSB offered him a job. He agreed, which surprised even his parents. His father asked him: Do you realize you won’t be able to travel abroad? I don’t really care, he responded.

4. Conclusions and Recommendations

As the world has seen in Ukraine, the Soviet military-industrial complex is back with a vengeance — only now, it is supplemented with cyber capabilities.

What we know about operational command and control in Russian cyber is limited, but as the history and analysis above has shown, we can draw four important conclusions.

First, Russia does not have a true cyber command. While the Presidential Administration and the Security Council coordinate cyber operations involving various agencies and non-state or quasi-state actors, they are not a cyber command in the US sense. There is no clear delineation of operational responsibility and no uniform system of reporting and accountability. Rather, Russia’s cyber-active agencies and actors are governed through a largely informal system of relationships in which political expediency may trump operational efficiency.

Second, the organizational, strategic, and cultural differences that characterize Russia’s various military and security agencies in the conventional field do not carry over into cyber operations. While their leadership may prefer not to, agencies such as the SVR and the GRU often find themselves attacking domestic cyber targets, while the FSB is active internationally.

Third, the lack of a true cyber command appears to mean that agencies tend to apply conventional approaches to cyber, rather than developing command-and-control approaches tailored to the cyber domain. While it is not clear that this has an adverse impact on efficacy, it further distinguishes patterns of cyber command in Russia from those found in the West. US and Western analysts must thus be careful not to assume that Russian structures and approaches mirror their own.

Fourth, Russia’s cyber-active state, quasi-state, and non-state cyber actors share roots in the Soviet and early post-Soviet SIGINT and cyber spheres — roots that continue to shape how Russian cyber functions to this day. This is reflected in the significant and continuing dependence of state actors on the private sector for recruitment, training, and technology, and in the fact that all actors recruit broadly from the same cohorts of specialists, with operatives sometimes moving fluidly from one agency to another. In that sense, structural distinctions between Russian cyber actors may be misleading.
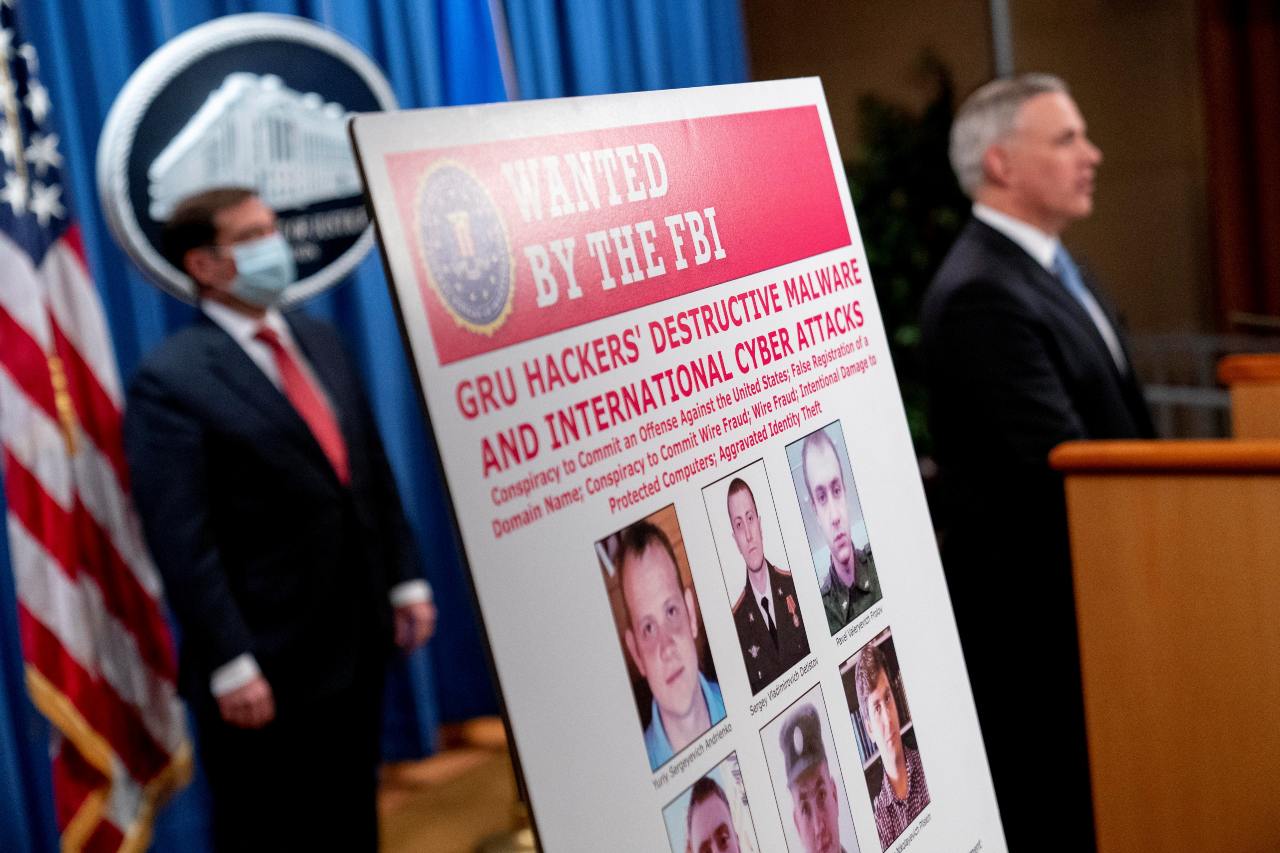
Photo: A poster showing six wanted Russian military intelligence officers is displayed as U.S. Attorney for the Western District of Pennsylvania Scott Brady, accompanied by Assistant Attorney General for the National Security Division John Demers, speaks at a news conference at the Department of Justice, in Washington, U.S., October 19, 2020. Credit: Andrew Harnik/Pool via REUTERS

Photo: A poster showing six wanted Russian military intelligence officers is displayed as U.S. Attorney for the Western District of Pennsylvania Scott Brady, accompanied by Assistant Attorney General for the National Security Division John Demers, speaks at a news conference at the Department of Justice, in Washington, U.S., October 19, 2020. Credit: Andrew Harnik/Pool via REUTERS

In the cyber arena, Russia’s biggest asset remains its cadres. The Soviet Union boasted the biggest engineer community in the world to serve its enormous military-industrial complex. Under Stalin, dozens of polytechnic schools were built across the country to train engineers, and networks of research facilities — secret and within the ostensibly civilian institutions — were funded for those engineers to contribute to the Soviet military and security services’ R&D.

When the Soviet Union collapsed, this sprawling system shook but didn’t break down. Some parts remained in the now independent countries, some fell into complete disarray due to lack of funding, but by and large, the parts within Russia survived the shock of the Soviet disintegration. The system did, however, experience a large hemorrhage of talent — many engineers went outside the tightly controlled world of the military-industrial complex to start a new life in private industry. Those engineers who chose the bright side launched Russian tech companies, including cybersecurity companies. The engineers, and their children, who chose the dark side, contributed to the emergence of the phenomenon of Russian hackers.

Under Putin, Russia’s intelligence community and the military were given political and financial resources to make use of that legacy. The polytechnic schools were given resources to reproduce talent, and new recruitment practices were adopted to make good use of those human resources which had gone private — both in the legal cyber business and in criminal hacker activities.

These days, Putin’s Kremlin relies on substantial cyber resources and a Soviet engineer culture that makes sure that enough talent and resources are available for Russia’s cyber operations on a global scale. The IT talent exodus from Russia is still underway, and the organizational competition for this talent between the services will likely only intensify, but there is not yet any indication that this has diminished or will diminish the threat posed by Russia’s cyber capabilities.

In the cyber arena, Russia’s biggest asset remains its cadres.

At least two things must be done to help contain the cyber threat from Russia.

Over the years, Western intelligence agencies accumulated substantial information about Russia’s cyber efforts. More of this data should be made available to the public, including information about the command-and-control systems, especially of the SVR. Greater transparency is needed, and intelligence sharing on key actors and their activities must be made a priority. Also, more transparency would help formulate more rigorous export controls to ensure Western tech is not enabling R&D of Russian cyber offensive operations.

The issue of Russian engineer training should also be addressed. In the foreseeable future, one cannot hope that Russian authorities will start a proper reform of the Russian education system. But Russian IT engineers and programmers are an essential part of the global effort in technology development; this is one of the achievements of globalization. It would be useful to set up STS (Science, Technology, and Society) courses, similar to the ones at the best US engineering schools, for Russian engineers working at Western companies. Educating Russian IT engineers on ethics would help bring a concept of the rule of law in the constantly changing world of cyber where the Russians are destined to play a key role no matter what political regime is in place in Moscow.

Acknowledgments

This report – Russian Cyberwarfare: Unpacking the Kremlin’s Capabilities – is part of CEPA’s ongoing work on Russia’s cyber operations and below-threshold threats. The authors extend their gratitude to the reviewers who provided insight and feedback on earlier drafts of this report. In particular, we thank for their invaluable comments and suggestions Sam Greene, Director for Democratic Resilience at CEPA; Jason Israel, Senior Fellow at CEPA; and Gavin Wilde, Senior Fellow at the Carnegie Endowment for International Peace. We are also grateful for the insights and contributions from the experts who attended CEPA’s roundtables in June and July and the research support from CEPA’s Research Assistant, Guga Chomakhidze. Finally, a special thank you to the entire CEPA team for their support and guidance on this report.

This publication was funded by the Russia Strategic Initiative, US European Command, Stuttgart, Germany. Opinions, arguments, viewpoints, and conclusions expressed in this work do not represent those of RSI, US EUCOM, the Department of Defense, or the US Government. This publication is cleared for public release.

Artboard 2

Categories
Saved Web Pages

Oppose FBI attack on Cuba Solidarity Committee

The FBI is expanding its efforts to intimidate Cuba solidarity supporters from Puerto Rico to the mainland, visiting or calling at least four people on the West Coast and Midwest over the last few weeks.

The harassment began in Puerto Rico over three days in late August when FBI agents visited or called nearly 60 people, largely participants in July’s Juan Rius Rivera Solidarity Brigade to Cuba. The annual brigade is organized by the Cuba Solidarity Committee on the island. Some FBI agents claimed that they were investigating “criminal activity” or alleged “infiltration” by Cuban security agents. At least 15 FBI agents were directly involved.

As soon as Milagros Rivera, president of the committee, learned of the visits and calls, she sent out an alert, letting people know that they don’t need to talk to the political police agents. “Our most important message,” she said, “is we are going to continue our united work to defeat the criminal U.S. blockade of Cuba.”

The committee organized a press conference and has won messages of support from dozens of organizations around the world.

Since then opponents in the U.S. of Washington’s economic war against Cuba have been contacted by the FBI. Two FBI agents on Sept. 20 visited the Los Angeles home of Mark Friedman, a member of the U.S. Hands Off Cuba Committee there. They claimed someone said he “would help them on the issue of Cuba.” Friedman wasn’t home.

The FBI has a long history of violating the constitutional rights and trying to disrupt the activities of labor unions, Black rights organizations, the Socialist Workers Party and anyone who opposes Washington’s war moves abroad.

Milagros Rivera will be the featured speaker at a public meeting in New York City Oct. 28 to denounce the FBI harassment. The evening meeting will take place at the First Spanish United Methodist Church (“The People’s Church”) in East Harlem.

Categories
Saved Web Pages

Walter Soriano: The Security Consultant for Russian Oligarchs, the CIA … and Diego Maradona?

imagebank_orig_orig_4dccd7836df846cc9290

Walter Soriano

Natasha Bertrand at Politico was out with a big story earlier this week about Walter Soriano, a mysterious Orthodox Jew who runs a security firm in London.

Bertrand reported that the Senate Intelligence Committee issued a subpoena to Soriano seeking his communications with Paul Manafort and Michael Flynn.

The subpoena, sent April 5, also seeks records of Soriano’s contacts with three Israeli private intelligence firms as well as any communications he may have had with Orbis Business Intelligence, a firm co-founded by the former British spy Christopher Steele.

The 51-year-old Soriano is unknown in the United States, but he’s a figure of intense speculation in Israel where his name surfaced more than a year ago in connection with a bribery investigation of Israeli Prime Minister Benjamin Netanyahu.

Israeli Kan TV news reported that Soriano was hired to dig up dirt on the investigators investigating Netanyahu. This work was given to subcontractors, some of whom worked for Israeli military intelligence:

This prompted Netanyahu to write a Facebook post insisting that he had not spoken to Soriano in eight years.

What intrigued me about Soriano was that Bertrand’s story linked him to Oleg Deripaska, whose connections to Paul Manafort were at the heart of Robert Mueller’s investigation into Russian interference in the 2016 election.

What hasn’t been reported in the United States is that Deripaska was a client of Soriano’s consultancy, USG Security Limited, according to a court filing by Israeli investigative journalist Raviv Drucker. (Soriano is suing Drucker in Israel for libel.) Drucker wrote that Soriano worked for Deripaska during his long-running legal feud in London with Michael Cherney, who has long faced allegations—which he has denied—that he and his brother, Lev, are connected to Russian organized crime.

Another oligarch, Roman Abramovich, also was a USG client, according to Drucker. USG helped Abramovich in his legal dispute in London with Boris Berezovsky, Drucker’s court filing states.

Drucker claims that USG’s subcontractors carried out “sophisticated surveillance, information gathering and data acquisition by various technological means, such as eavesdropping, hacking, and so on.”

On its website, USG says that its consultants are “all former members of the world’s elite intelligence units, military forces and security organizations, with vast knowledge and practical experience.”

This sounds very much like the work of the three private Israeli security firms who are mentioned in the subpoena: Psy Group, Wikistrat, and Black Cube. Founded by former Israeli military intelligence officers, Black Cube has used operatives with false identities to investigate journalists, victims of Harvey Weinstein, and former Obama staffer Ben Rhodes. Published reports claim Trump aides hired Black Cube for a “dirty ops” campaign to discredit Rhodes and other supporters of the Iran nuclear deal. (Black Cube denied working for Trump.)

Another Soriano client is Dmitry Rybolovlev, another Russian billionaire who purchased a Florida mansion from Trump in 2008 for $95 million. Trump had purchased the mansion for $41 million four years earlier.

Rybolovlev hired Soriano to spy on art dealer Yves Bouvier, according to Drucker and an investigation by Le Point, a French newsweekly. Le Point also obtained correspondence from Soriano to Rybolovlev suggesting he was also hired to deal with problems at the football club the oligarch owns, AS Monaco. (See “L’étrange M. Soriano,” Le Point, February 7 2019.)

The football connection is an interesting thread in this strange world because someone named Walter Soriano emerged in 2010 — the same year that USG Security Limited went into business — as the UK representative of former Argentinian superstar Diego Maradona.

Diego Maradona

“I think Diego would be very open to the idea of coming to England and managing Aston Villa,” a reporter for the Sunday Mercury quoted “Walter Soriano” as saying.

The real Walter Soriano was at one time a partner in a now defunct UK firm called Football Universe Limited. And like Maradona, Soriano is a native Argentinian, the tireless blogger Richard Silverstein reported. (An Israeli judge threw out Soriano’s lawsuit against Silverstein.)

An earlier version of USG’s website names Soriano as director of operations and Simon Bird simply as “UK operations.” The equally mysterious Mr. Bird, who is 76 and not to be confused with an English actor of the same name, gave an address of Ware House in Lyme Regis, a manor immortalized in the film The French Lieutenant’s Woman. Bird is described as a historian and a longtime partner of Winston Churchill’s granddaugher-in-law.

Both Bird and Soriano were directors of a now-defunct UK firm, Universe Security Group, whose board included Nahum Admoni, a former head of Mossad; Uri Sagi, former head of IDF intelligence; and Albert Raes, formerly Belgium’s top spy. (Issac Molho, a trusted advisor to Netanyahu caught up in the prime minister’s scandals, received about $200,000 in “finder’s fees” from the company.)

Update: A reader who asked not to be named pointed out that Molho did not just receive finder’s fees. He owned 10 percent of the company, according to a letter of intent he signed in 2003. Soriano was the majority shareholder.

In 2003, the Panama Maritime Authority, which manages the world’s largest ship register, selected Universe Security Group as one of three “recognized security organizations” to approve ship security plans. Soriano told Lloyd’s List that company operatives come mainly from the UK, Belgium, Israel, Central and South America, North Africa and the US.

A sharp-eyed Twitter user, @brazencapital, pointed out something I had read many years ago and since forgotten. One of Universe Security Group’s contacts was Kyle “Dusty” Foggo, formerly the No. 3 at the CIA who went to prison in the scandal surrounding Congressman Randy “Duke” Cunningham. (Foggo was one of the subjects in my first book, Feasting on the Spoils.)

Buried in Foggo’s sentencing memorandum from 2008 is a statement from a CIA contractor named Joel Combs:

Sentencing memo, US v Foggo

Universe Security’s reputation suffered a fatal blow in 2009 when one of its customers was robbed, according to an administrator’s report. (The client was not identified in the report but Israeli media reports named Graff diamonds in London.) Admoni, Sagi and Raes all resigned from the company en masse. The company went into liquidation; its assets were acquired by Soriano and Bird’s newly-formed USG Security.

There’s more. Soriano’s USG Security also surfaced in a dispute between wealthy London property developers the Candy brothers and British businessman Mark Holyoake.

“I have reliable information that USG Security has been hired by [Ed Candy] for (sic) investigate and monitor my family, my colleagues and myself,” Holyoake told a London court. He described USG as a “military-based ‘security consultancy and security services provider.’” (See Holyoake v Candy, Queen’s Bench Division)

Holyoake declined to reveal who passed him this information saying it related to security arrangements for his family and “could have consequences for the safety of my source if revealed.” Candy’s representative denied hiring USG.

During trial, Holyoake’s wife testified that among the men in the Candys’ “extended circle who have died mysteriously” is Boris Berezovsky, the exiled Russian oligarch in London who became a fierce critic of Vladimir Putin.

Berezovsky lost his high stakes London court battle with Roman Abramovich in 2012 over control over a major Russian oil company. Seven months later, Berezovsky was found dead in his shower with a scarf around his neck. A coroner could not reach a verdict on the death.

The mysterious Mr. Soriano is much than he seems. Connected to the prime minister, deeply tied to the Israeli security establishment, he adds to the intrigue surrounding Trump and Russia.

WP Radio
WP Radio
OFFLINE LIVE